

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed LinkedIn
If you run security for other companies, here is a way to add software supply chain and application security to what you deliver. Safeguard's partner program has a track for MSSPs and managed security providers. Offer Safeguard as part of a managed detection, managed compliance…
Read the full postHide the full post
If you run security for other companies, here is a way to add software supply chain and application security to what you deliver. Safeguard's partner program has a track for MSSPs and managed security providers. Offer Safeguard as part of a managed detection, managed compliance or managed VAPT service, and operate the platform on behalf of your clients. Consultancies can also resell it, or white-label it under their own brand and keep the customer relationship, pricing and UI. What partners get: Partners earn a 30% margin A partner portal with sandbox tenants for POC scoping and an asset library Training, battlecards and demo environments Open worldwide Audit firms can join too, through referral and co-marketing. There is no commission, so audit independence stays intact. Apply on the partners page and we book a 30 minute fit call: https://lnkd.in/gE6e8Y34 #MSSP #Partners #ChannelPartners #AppSec
- Instagram
Run security for other companies? Safeguard's partner program has a track for MSSPs and consultancies: operate the platform for your clients as part of a managed service, or resell or white-label it. Partners earn a 30% margin. Open worldwide. Link in bio: http://safeguard.sh/co…
Read the full postHide the full post
Run security for other companies? Safeguard's partner program has a track for MSSPs and consultancies: operate the platform for your clients as part of a managed service, or resell or white-label it. Partners earn a 30% margin. Open worldwide. Link in bio: http://safeguard.sh/company/partners #MSSP #Partners #CyberSecurity #ChannelPartners #AppSec
- X
MSSPs and consultancies: run Safeguard for your clients as part of a managed service, or resell or white-label it. Partners earn a 30% margin. Open worldwide. https://t.co/hA4CpKHRBM https://t.co/hBXgRFzqDt
Read the full postHide the full post
MSSPs and consultancies: run Safeguard for your clients as part of a managed service, or resell or white-label it. Partners earn a 30% margin. Open worldwide. https://t.co/hA4CpKHRBM https://t.co/hBXgRFzqDt
 YouTubeVideo
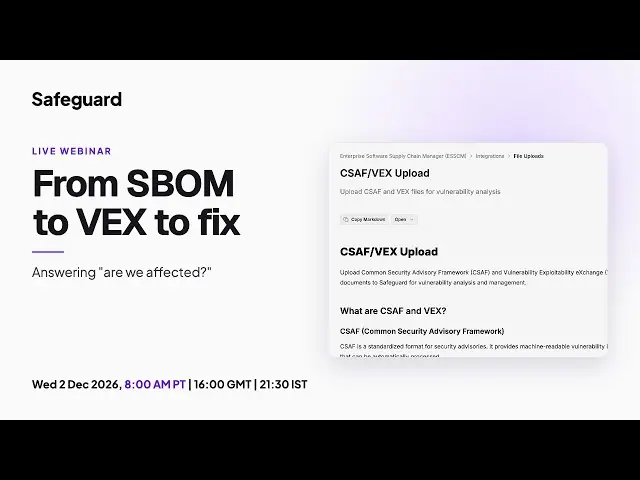
Live webinar, episode 1 of our monthly series. A customer, an auditor or your own CISO asks: are we affected by this CVE? In this session we show how to answer with an SBOM, a VEX statement and a reviewed fix, then a short live demo and 15 minutes of live Q and A. Wednesday 2 De…
Read the full postHide the full post
Live webinar, episode 1 of our monthly series. A customer, an auditor or your own CISO asks: are we affected by this CVE? In this session we show how to answer with an SBOM, a VEX statement and a reviewed fix, then a short live demo and 15 minutes of live Q and A. Wednesday 2 December 2026: 8:00 AM PT, 11:00 AM ET, 16:00 GMT, 17:00 CET, 21:30 IST. About 50 minutes. Presenter: Hritik Kumar Sharma, Founder, Safeguard. Moderator: John. Ask your questions in the live chat. Overflow Q and A on Discord: https://discord.gg/QBC9bekpz Product demos: https://safeguard.sh/demos?utm_source=youtube&utm_medium=live&utm_campaign=webinar-2026-12-sbom-vex-fix Docs: https://docs.safeguard.sh Topics: SBOM, VEX, CSAF, SPDX, CycloneDX, reachability analysis, fix pull requests, software supply chain security.
 LinkedIn
New CVEs, CISA KEV additions and malicious npm and PyPI package advisories land all day. Who has time to watch every feed? Safeguard Threat Radar is live on YouTube, 24/7. It brings public advisories together in one live view, so you can see what is new at a glance. Every item c…
Read the full postHide the full post
New CVEs, CISA KEV additions and malicious npm and PyPI package advisories land all day. Who has time to watch every feed? Safeguard Threat Radar is live on YouTube, 24/7. It brings public advisories together in one live view, so you can see what is new at a glance. Every item comes from public sources. Open it on a second screen: https://lnkd.in/gvFxkf8p
- Instagram
Safeguard Threat Radar is live, 24/7. New CVEs, CISA KEV additions and malicious npm and PyPI advisories in one live feed, from public sources. Link in bio (YouTube, live now).
Read the full postHide the full post
Safeguard Threat Radar is live, 24/7. New CVEs, CISA KEV additions and malicious npm and PyPI advisories in one live feed, from public sources. Link in bio (YouTube, live now).
- Facebook
Safeguard Threat Radar is live on YouTube, 24/7. A live view of new CVEs, CISA KEV additions and malicious npm and PyPI package advisories, all from public sources. Handy on a second screen. Watch it here: https://na2.hubs.ly/H08L9XL0
Read the full postHide the full post
Safeguard Threat Radar is live on YouTube, 24/7. A live view of new CVEs, CISA KEV additions and malicious npm and PyPI package advisories, all from public sources. Handy on a second screen. Watch it here: https://na2.hubs.ly/H08L9XL0
- X
Safeguard Threat Radar is live on YouTube, 24/7: new CVEs, CISA KEV additions and malicious npm and PyPI advisories in one live feed, from public sources. https://t.co/uINk7n27Mk https://t.co/QL8V6oSRJh
 LinkedIn
Is Safeguard SOC 2 compliant? Six minutes, straight answers. Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. Mira asks the questions a vendor review asks, and Cal answers from our published pages: Safeguard is SOC 2 Type I and Type II audited, what a readi…
Read the full postHide the full post
Is Safeguard SOC 2 compliant? Six minutes, straight answers. Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. Mira asks the questions a vendor review asks, and Cal answers from our published pages: Safeguard is SOC 2 Type I and Type II audited, what a readiness score is and is not, how to automate evidence without the screenshot sprint, and what to ask any security vendor for. Mira and Cal are AI voices. The script is written by the Safeguard team and checked against our published research. Listen on Spotify: https://lnkd.in/gqdBNBuz #SecurityPodcast #Compliance #SOC2
- Facebook
Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. Six minutes on the questions a vendor review asks: is Safeguard SOC 2 compliant, do you need an SBOM for SOC 2, and how do you automate evidence without the screenshot sprint. Mira and Cal are AI voices; the…
Read the full postHide the full post
Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. Six minutes on the questions a vendor review asks: is Safeguard SOC 2 compliant, do you need an SBOM for SOC 2, and how do you automate evidence without the screenshot sprint. Mira and Cal are AI voices; the script is written by the Safeguard team. Listen on Spotify: https://na2.hubs.ly/H08KyNk0
- Instagram
Is Safeguard SOC 2 compliant? Six minutes, straight answers. Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. The questions a vendor review asks, answered from our published pages, plus how to automate evidence without the screenshot sprint. Mira and Cal ar…
Read the full postHide the full post
Is Safeguard SOC 2 compliant? Six minutes, straight answers. Ask Safeguard, Ep 4 is live: SOC 2 and compliance, what is true today. The questions a vendor review asks, answered from our published pages, plus how to automate evidence without the screenshot sprint. Mira and Cal are AI voices. The script is written by the Safeguard team. Link in bio (Spotify). #securitypodcast #compliance #soc2 #appsec
- X
Is Safeguard SOC 2 compliant? Ask Safeguard Ep 4 answers the vendor review questions in 6 minutes. AI voices. https://t.co/SwqmOvsDXn https://t.co/S1ZcTtBn3w
- YouTubeVideo
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received d…
Read the full postHide the full post
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received date, who checked identity, which systems were searched, who reviewed the package, and the day the answer went out. They explain the one month deadline in Article 12 and the extension rule, how to confirm who is asking without collecting a passport scan, why logs with IP addresses count, what to do about backups when someone asks for erasure, how to correct data and tell the recipients, what data portability covers, and what a record of processing is for. They also cover the controller and processor question for a company that sells to businesses, and where Safeguard fits on the software evidence side without making anyone compliant. Before that, three stories: the noyb complaints against Scale AI filed on 27 October (allegations, with the company's response), the French regulator's fine against Extia over erasure requests, and the draft EDPB guidelines on fines that are open for comment until 13 November. Theo asks whether your deletion button really deletes, and the episode ends with a checklist for before your window opens. If you run a small software company and need to answer GDPR data subject requests, this episode covers the one month deadline under Article 12, identity checks, the right of access, the right to erasure and backups, rectification, data portability, the record of processing under Article 30, controller and processor roles, and the audit evidence a regulator or customer reviewer asks to see. It also looks at EDPB draft fining guidelines and recent enforcement by the CNIL. Topics: GDPR, data subject access request, DSAR, right to erasure, data portability, record of processing, controller and processor, audit evidence, audit readiness, EDPB, CNIL, noyb, Scale AI, Extia. Chapters: 00:00 Cold open 00:50 Intro 01:25 News: noyb and Scale AI, the Extia fine, the EDPB fining guidelines 05:18 Audit story: the Friday inbox 07:42 Deep dive: the one month clock, access, erasure, backups and the record 14:34 Practitioner corner 15:33 Checklist: before the next request 17:08 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 How to answer a GDPR data subject access request step by step: https://safeguard.sh/resources/blog/how-to-answer-a-gdpr-dsar-step-by-step?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 DSAR export pipeline architecture: https://safeguard.sh/resources/blog/dsar-export-pipeline-architecture?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Verify a requester's identity without collecting more data: https://safeguard.sh/resources/blog/verify-requester-identity-without-collecting-more-data?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Erasure requests and backups: what to do: https://safeguard.sh/resources/blog/erasure-requests-and-backups-what-to-do?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Rectification requests: propagate corrections: https://safeguard.sh/resources/blog/rectification-requests-propagate-corrections?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Data portability, Article 20: export format choices: https://safeguard.sh/resources/blog/data-portability-article-20-export-format-choices?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 The Article 30 record of processing: the engineering view: https://safeguard.sh/resources/blog/ropa-article-30-fields-engineering-view?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Is an IP address in a log personal data?: https://safeguard.sh/resources/blog/is-an-ip-address-in-a-log-personal-data-gdpr?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR for VPs of engineering: requests, deletion and transfers: https://safeguard.sh/resources/blog/gdpr-for-vps-of-engineering-requests-deletion-and-transfers?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR Article 32 and Article 28 evidence in the Safeguard compliance suite: https://safeguard.sh/resources/blog/gdpr-article-32-and-article-28-evidence-in-the-safeguard-compliance-suite?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Listen on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03
 Instagram
Safeguard Podcasts 24/7 is live on YouTube. Every episode on a loop, so there is always something to listen to while you work. Link in bio (YouTube, live now).
Read the full postHide the full post
Safeguard Podcasts 24/7 is live on YouTube. Every episode on a loop, so there is always something to listen to while you work. Link in bio (YouTube, live now).
- LinkedIn
Every podcast episode we have made, on a loop, all day and all night. Safeguard Podcasts 24/7 is live on YouTube. Software supply chain security, dependency fixes, audits and patching, explained in plain language. Leave it running while you work, or jump in whenever you have a f…
Read the full postHide the full post
Every podcast episode we have made, on a loop, all day and all night. Safeguard Podcasts 24/7 is live on YouTube. Software supply chain security, dependency fixes, audits and patching, explained in plain language. Leave it running while you work, or jump in whenever you have a few minutes. It is on right now: https://lnkd.in/gwXmWEZf
- Facebook
Safeguard Podcasts 24/7 is live on YouTube. Every one of our podcast episodes plays on a loop, so there is always something to listen to while you work, commute or wait for a build. Tune in: https://na2.hubs.ly/H08L9V10
Read the full postHide the full post
Safeguard Podcasts 24/7 is live on YouTube. Every one of our podcast episodes plays on a loop, so there is always something to listen to while you work, commute or wait for a build. Tune in: https://na2.hubs.ly/H08L9V10
- X
Safeguard Podcasts 24/7 is live on YouTube. Every podcast episode we have made, on a loop. Security talk for your desk or your commute. https://t.co/RZYXJYE0hm https://t.co/8jZFBA4Fr3
 LinkedIn
Is it safe to let a tool auto-merge your dependency fixes? And who signs off on a pull request that a tool wrote? Ask Safeguard, Season 1, Episode 5, "AI fixes: how they stay safe", is out on YouTube. Mira asks the questions teams raise before they let automatic fixes near their…
Read the full postHide the full post
Is it safe to let a tool auto-merge your dependency fixes? And who signs off on a pull request that a tool wrote? Ask Safeguard, Season 1, Episode 5, "AI fixes: how they stay safe", is out on YouTube. Mira asks the questions teams raise before they let automatic fixes near their repositories, and Cal answers: human review by default, opt in auto-merge behind passing CI, and your tests run before a pull request opens. Watch the episode: https://lnkd.in/grd6qhtz
- Instagram
New on YouTube: Ask Safeguard S1E5, "AI fixes: how they stay safe". Is auto-merging dependency fixes safe, and who approves a pull request a tool wrote? Link in bio (YouTube, out now).
Read the full postHide the full post
New on YouTube: Ask Safeguard S1E5, "AI fixes: how they stay safe". Is auto-merging dependency fixes safe, and who approves a pull request a tool wrote? Link in bio (YouTube, out now).
- Facebook
New on YouTube: Ask Safeguard, Season 1, Episode 5, "AI fixes: how they stay safe". Is auto-merging dependency fixes safe, and who approves a pull request a tool wrote? About six minutes, straight answers. Watch it here: https://na2.hubs.ly/H08Lb0Q0
Read the full postHide the full post
New on YouTube: Ask Safeguard, Season 1, Episode 5, "AI fixes: how they stay safe". Is auto-merging dependency fixes safe, and who approves a pull request a tool wrote? About six minutes, straight answers. Watch it here: https://na2.hubs.ly/H08Lb0Q0
- X
New on Ask Safeguard: "AI fixes: how they stay safe". Is auto-merging dependency fixes safe, and who approves a pull request a tool wrote? Six minutes, straight answers. https://t.co/Jl2OuaoB8Y https://t.co/OpvQs90BmI
 Instagram
A new minimal base image, or fixes for the images you already run? Chainguard Images and Wolfi vs Safeguard Gold. We are a competitor, so the post credits Chainguard's larger catalog and says when to pick it. As of 28 October 2026. Link in bio: safeguard.sh/resources/blog
Read the full postHide the full post
A new minimal base image, or fixes for the images you already run? Chainguard Images and Wolfi vs Safeguard Gold. We are a competitor, so the post credits Chainguard's larger catalog and says when to pick it. As of 28 October 2026. Link in bio: safeguard.sh/resources/blog
 InstagramVideo
Which 5 things do I fix first? Ask Claude in plain English with Safeguard added from the connector directory. Known exploited and reachable-with-a-fix first, severity only breaks ties, one upgrade per package. Read only by default; a person makes the change. Link in bio: http://…
Read the full postHide the full post
Which 5 things do I fix first? Ask Claude in plain English with Safeguard added from the connector directory. Known exploited and reachable-with-a-fix first, severity only breaks ties, one upgrade per package. Read only by default; a person makes the change. Link in bio: http://safeguard.sh/resources/blog #AppSec #DevSecOps #VulnerabilityManagement
 LinkedInVideo
Which 5 things do I fix first? Ask Claude that in plain English, with Safeguard added from Claude's connector directory, and you get a short list of upgrades, not a wall of CVEs. Claude reads your Safeguard vulnerability data and: 1. Puts known exploited flaws at the top, along…
Read the full postHide the full post
Which 5 things do I fix first? Ask Claude that in plain English, with Safeguard added from Claude's connector directory, and you get a short list of upgrades, not a wall of CVEs. Claude reads your Safeguard vulnerability data and: 1. Puts known exploited flaws at the top, along with anything reachable that already has a fix 2. Uses the severity score only to break ties 3. Groups every vulnerability on one package into one upgrade, and flags major version jumps The connector is read only by default. Claude ranks the list and drafts the ticket text. A person makes the change. Vulnerability management with EPSS and KEV is GA. Reachability analysis is GA. Full walkthrough: https://lnkd.in/gbA-SZUx #AppSec #VulnerabilityManagement #DevSecOps
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.