

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on YouTube
RSS feed YouTubeVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compa…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compatible, Anthropic Messages or Gemini API) and where it runs (SaaS in the US, EU (Frankfurt) or Gov, a private VPC, on-prem, or air-gapped with Safeguard's models inside). Honest note: closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models, and a self-hosted endpoint must be reachable from Safeguard SaaS. Where your code and data go: https://na2.hubs.ly/H08FzbG0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI. Stock footage: Mixkit (Mixkit Stock Video Free License). Product footage: Safeguard docs, recorded read-only. #appsec #supplychainsecurity #dataresidency
 YouTubeVideo
A new blocking rule that breaks every build tends to get switched off. In Safeguard each policy has one action: Block, Warn or Notify. A warn lets the gate pass and names the policy. Fix what it finds, flip the same rule to Block, and let one CI step fail the build when the gate…
Read the full postHide the full post
A new blocking rule that breaks every build tends to get switched off. In Safeguard each policy has one action: Block, Warn or Notify. A warn lets the gate pass and names the policy. Fix what it finds, flip the same rule to Block, and let one CI step fail the build when the gate fails. Footage: Mixkit stock (free license), Safeguard app gates view (our own recording). Policies vs gates vs guardrails: https://na2.hubs.ly/H08LgPc0 #DevSecOps #AppSec #Shorts
- YouTubeVideo
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. The Mac builds are signed and notarized. Windows and Linux installers list SHA…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. The Mac builds are signed and notarized. Windows and Linux installers list SHA-256 checksums on the download page. Footage: Mixkit stock (free license), recording of https://na2.hubs.ly/H08LgFP0. Download: https://na2.hubs.ly/H08LgFQ0 #AppSec #DevSecOps #Shorts
 YouTubeVideo
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received d…
Read the full postHide the full post
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received date, who checked identity, which systems were searched, who reviewed the package, and the day the answer went out. They explain the one month deadline in Article 12 and the extension rule, how to confirm who is asking without collecting a passport scan, why logs with IP addresses count, what to do about backups when someone asks for erasure, how to correct data and tell the recipients, what data portability covers, and what a record of processing is for. They also cover the controller and processor question for a company that sells to businesses, and where Safeguard fits on the software evidence side without making anyone compliant. Before that, three stories: the noyb complaints against Scale AI filed on 27 October (allegations, with the company's response), the French regulator's fine against Extia over erasure requests, and the draft EDPB guidelines on fines that are open for comment until 13 November. Theo asks whether your deletion button really deletes, and the episode ends with a checklist for before your window opens. If you run a small software company and need to answer GDPR data subject requests, this episode covers the one month deadline under Article 12, identity checks, the right of access, the right to erasure and backups, rectification, data portability, the record of processing under Article 30, controller and processor roles, and the audit evidence a regulator or customer reviewer asks to see.
 YouTubeVideo
Your agent is about to get a new tool. Who wrote it, and what can it touch? Look the MCP server up on Gold Open Source (https://na2.hubs.ly/H08LgDx0) first. It is free and needs no login. The page shows the publisher namespace, the version, hosted endpoint or installable package…
Read the full postHide the full post
Your agent is about to get a new tool. Who wrote it, and what can it touch? Look the MCP server up on Gold Open Source (https://na2.hubs.ly/H08LgDx0) first. It is free and needs no login. The page shows the publisher namespace, the version, hosted endpoint or installable package, the transport, the source repository and a license note. A package means their code runs on your machine, so check what it depends on. Gold does not list tools or scopes, so read those yourself in a test client. Full routine: https://na2.hubs.ly/H08LgF30 Stock footage: Mixkit (Mixkit Stock Video Free License). Page recordings: https://na2.hubs.ly/H08LgF40, public pages. #MCP #AIsecurity #Shorts
- YouTubeVideo
Day one on a new team. Sam installs one extension, signs in, and a warning shows up on a package she didn't choose. Mira and Cal walk through her first ten minutes with Safeguard in the editor and in the chat window: install the VS Code or JetBrains extension, sign in with the d…
Read the full postHide the full post
Day one on a new team. Sam installs one extension, signs in, and a warning shows up on a package she didn't choose. Mira and Cal walk through her first ten minutes with Safeguard in the editor and in the chat window: install the VS Code or JetBrains extension, sign in with the device flow, pick a remediation strategy, apply one fix, read the diff, and hand the pull request to a teammate. Then they connect Claude or ChatGPT to Safeguard's hosted MCP server and see what a fresh workspace can and cannot do. In the news, three October stories about things that ran before a person looked: a malicious LiteLLM release on PyPI (JFrog, 21 Oct; LiteLLM's own account, 23 Oct), a planted AGENTS.md that led Codex to try installing a malicious package (Forever Security, 25 Oct), and an npm worm that armed GitHub repositories with startup hooks for Claude, Cursor and VS Code (JFrog, 26 Oct). Under the hood, the inline Package Firewall check for typosquatting, dependency confusion and malicious package names, why a hosted MCP server means there is no package to install, and what to ask about any AI coding agent. Theo brings one setting, and the episode ends with a try-this-today checklist for secure coding with AI. Topics: AI coding agents, secure coding with AI, VS Code extension, JetBrains plugin, MCP server, MCP security, Claude connector, ChatGPT, Cursor, Claude Code, OpenAI Codex, LiteLLM, JFrog, Forever Security, AGENTS.md, npm worm, malicious packages, typosquatting, dependency confusion, supply chain security, code review of AI generated code. Chapters: 00:00 Cold open 00:28 Intro 00:51 News: LiteLLM 1.107.0, a planted AGENTS.md, and the npm worm hooks 04:05 Sam's first ten minutes: editor and chat 08:07 Under the hood 10:02 Theo's one setting 10:52 Try this today 11:58 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 Downloads (editor extensions): https://safeguard.sh/download?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 IDE Support documentation: https://docs.safeguard.sh/docs/ide-support?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 Connect Claude to Safeguard: https://docs.safeguard.sh/docs/mcp/claude?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 Connect ChatGPT to Safeguard: https://docs.safeguard.sh/docs/mcp/openai?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 Safeguard blog: https://safeguard.sh/blog?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02 Listen on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx?utm_source=podcast&utm_medium=video&utm_campaign=permission-prompt&utm_content=ep02
- YouTubeVideo
A scan in a separate job pulls from a registry, so the image is already pushed. Scan in the build job instead: the Safeguard CLI reads the local image, checks OS packages, the base image and app dependencies, and only results leave the runner. Fail the step on a severity, push o…
Read the full postHide the full post
A scan in a separate job pulls from a registry, so the image is already pushed. Scan in the build job instead: the Safeguard CLI reads the local image, checks OS packages, the base image and app dependencies, and only results leave the runner. Fail the step on a severity, push only what passed, and scan again at deploy. Full guide: https://na2.hubs.ly/H08LgzL0 People footage: Mixkit stock (Mixkit Stock Video Free License). #DevSecOps #ContainerSecurity #Shorts
 YouTubeVideo
PostgreSQL 14 gets its final release on 12 November 2026, per https://na2.hubs.ly/H08LcTv0. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run: the main cluster, CI containers, migration jobs, replicas and vendor appliances. Apply the final…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November 2026, per https://na2.hubs.ly/H08LcTv0. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run: the main cluster, CI containers, migration jobs, replicas and vendor appliances. Apply the final 14 release when it ships, then plan the move to 18. Footage: PostgresConf South Africa 2018 opening, video by Malcolm McLean, CC BY 4.0 (https://na2.hubs.ly/H08LcV70). Mixkit stock (free license). Local terminal recording and https://na2.hubs.ly/H08LcTw0 screen recording. Write-up: https://na2.hubs.ly/H08LcTx0 #PostgreSQL #DevOps #Shorts
- YouTubeVideo
Is there a document editing app on your file server that you installed once and forgot? CISA put one on its exploited list on 23 October, and the advisory says switching it off is not enough. This Patch Monday briefing covers four stories from 23 to 30 October 2026, each with wh…
Read the full postHide the full post
Is there a document editing app on your file server that you installed once and forgot? CISA put one on its exploited list on 23 October, and the advisory says switching it off is not enough. This Patch Monday briefing covers four stories from 23 to 30 October 2026, each with what happened, who is stuck with it right now, and one switch to flip on Monday morning: turn it off, narrow it, or set it on purpose. A vulnerability management and patch management story: CVE-2026-110447 in the Collabora Online Built-in CODE Server app for Nextcloud, on CISA's Known Exploited Vulnerabilities list since 23 October, and why Collabora's advisory says to update or remove the app. A credential theft story: Wiz Research's 25 October report on Gheist, a campaign that uses stolen GitHub tokens to plant workflows that print repository secrets, and how to narrow the tokens that can reach your repositories. A compliance story: the Department of Homeland Security notice of 30 October on an order to remove Acronis products from federal civilian systems, and the question it raises about every tool that runs with privileged access. And an AI agent security story: Anthropic's 26 October advisory for CVE-2026-88968, a race condition in the Claude Code Edit tool that could let a file be written outside the workspace on macOS. About eight minutes, for security engineers, AppSec leads, platform teams, compliance leads and CISOs. Topics: CVE-2026-110447, CVE-2026-88968, Collabora Online, Nextcloud, CISA KEV, Known Exploited Vulnerabilities, Gheist, GitHub tokens, GitHub Actions secrets, Wiz Research, Acronis, Federal Acquisition Supply Chain Security Act, Department of Homeland Security, Claude Code, Anthropic, vulnerability management, patch management, least privilege, software supply chain attack, compliance, AI agent security, security podcast, cybersecurity podcast, AppSec podcast, DevSecOps podcast, security engineer, CISO, Safeguard Chapters: 00:00 Cold open 00:15 Intro 00:41 Story 1: Collabora Built-in CODE Server for Nextcloud, CVE-2026-110447 on KEV 02:06 Story 2: Gheist and stolen GitHub tokens 03:40 Story 3: the DHS order on Acronis products 05:13 Story 4: the Claude Code Edit tool advisory, CVE-2026-88968 06:44 What to do Monday 07:12 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Safeguard blog: https://safeguard.sh/blog?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Your copied workflow has no permissions block: what should you do: https://safeguard.sh/resources/blog/a-starter-workflow-has-no-permissions-block-add-one?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 How do you apply least privilege to AI agents: https://safeguard.sh/resources/blog/ai-agents-and-least-privilege-checklist?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02 Listen on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn?utm_source=podcast&utm_medium=video&utm_campaign=patch-monday&utm_content=ep02
- YouTubeVideo
A quick answer from Ask Safeguard, Ep 5: nobody has to read every fix, because only the exceptions need a person. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
Read the full postHide the full post
A quick answer from Ask Safeguard, Ep 5: nobody has to read every fix, because only the exceptions need a person. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
- YouTubeVideo
A quick answer from Ask Safeguard, Ep 5: a fix is only as well checked as your tests, so green means more when your test suite is good. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
Read the full postHide the full post
A quick answer from Ask Safeguard, Ep 5: a fix is only as well checked as your tests, so green means more when your test suite is good. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
- YouTubeVideo
A quick answer from Ask Safeguard, Ep 5: routine fixes can merge on their own, while risky ones keep a human review. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
Read the full postHide the full post
A quick answer from Ask Safeguard, Ep 5: routine fixes can merge on their own, while risky ones keep a human review. Full episode: https://youtu.be/pkGLATpfbDQ #Shorts
 YouTubeVideo
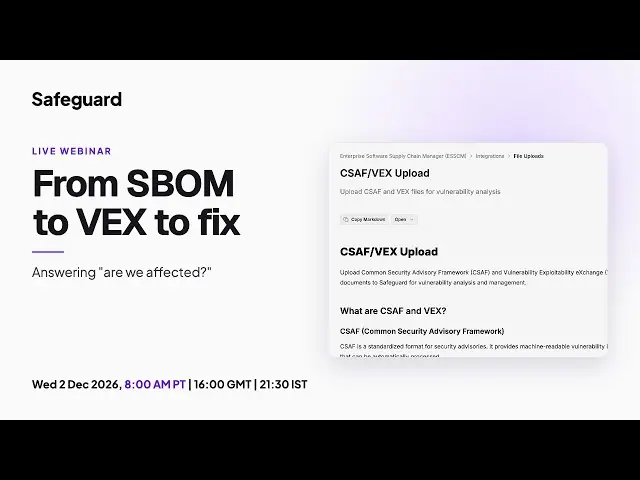
Live webinar, episode 1 of our monthly series. A customer, an auditor or your own CISO asks: are we affected by this CVE? In this session we show how to answer with an SBOM, a VEX statement and a reviewed fix, then a short live demo and 15 minutes of live Q and A. Wednesday 2 De…
Read the full postHide the full post
Live webinar, episode 1 of our monthly series. A customer, an auditor or your own CISO asks: are we affected by this CVE? In this session we show how to answer with an SBOM, a VEX statement and a reviewed fix, then a short live demo and 15 minutes of live Q and A. Wednesday 2 December 2026: 8:00 AM PT, 11:00 AM ET, 16:00 GMT, 17:00 CET, 21:30 IST. About 50 minutes. Presenter: Hritik Kumar Sharma, Founder, Safeguard. Moderator: John. Ask your questions in the live chat. Overflow Q and A on Discord: https://discord.gg/QBC9bekpz Product demos: https://safeguard.sh/demos?utm_source=youtube&utm_medium=live&utm_campaign=webinar-2026-12-sbom-vex-fix Docs: https://docs.safeguard.sh Topics: SBOM, VEX, CSAF, SPDX, CycloneDX, reachability analysis, fix pull requests, software supply chain security.
- YouTubeVideo
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received d…
Read the full postHide the full post
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received date, who checked identity, which systems were searched, who reviewed the package, and the day the answer went out. They explain the one month deadline in Article 12 and the extension rule, how to confirm who is asking without collecting a passport scan, why logs with IP addresses count, what to do about backups when someone asks for erasure, how to correct data and tell the recipients, what data portability covers, and what a record of processing is for. They also cover the controller and processor question for a company that sells to businesses, and where Safeguard fits on the software evidence side without making anyone compliant. Before that, three stories: the noyb complaints against Scale AI filed on 27 October (allegations, with the company's response), the French regulator's fine against Extia over erasure requests, and the draft EDPB guidelines on fines that are open for comment until 13 November. Theo asks whether your deletion button really deletes, and the episode ends with a checklist for before your window opens. If you run a small software company and need to answer GDPR data subject requests, this episode covers the one month deadline under Article 12, identity checks, the right of access, the right to erasure and backups, rectification, data portability, the record of processing under Article 30, controller and processor roles, and the audit evidence a regulator or customer reviewer asks to see. It also looks at EDPB draft fining guidelines and recent enforcement by the CNIL. Topics: GDPR, data subject access request, DSAR, right to erasure, data portability, record of processing, controller and processor, audit evidence, audit readiness, EDPB, CNIL, noyb, Scale AI, Extia. Chapters: 00:00 Cold open 00:50 Intro 01:25 News: noyb and Scale AI, the Extia fine, the EDPB fining guidelines 05:18 Audit story: the Friday inbox 07:42 Deep dive: the one month clock, access, erasure, backups and the record 14:34 Practitioner corner 15:33 Checklist: before the next request 17:08 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 How to answer a GDPR data subject access request step by step: https://safeguard.sh/resources/blog/how-to-answer-a-gdpr-dsar-step-by-step?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 DSAR export pipeline architecture: https://safeguard.sh/resources/blog/dsar-export-pipeline-architecture?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Verify a requester's identity without collecting more data: https://safeguard.sh/resources/blog/verify-requester-identity-without-collecting-more-data?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Erasure requests and backups: what to do: https://safeguard.sh/resources/blog/erasure-requests-and-backups-what-to-do?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Rectification requests: propagate corrections: https://safeguard.sh/resources/blog/rectification-requests-propagate-corrections?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Data portability, Article 20: export format choices: https://safeguard.sh/resources/blog/data-portability-article-20-export-format-choices?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 The Article 30 record of processing: the engineering view: https://safeguard.sh/resources/blog/ropa-article-30-fields-engineering-view?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Is an IP address in a log personal data?: https://safeguard.sh/resources/blog/is-an-ip-address-in-a-log-personal-data-gdpr?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR for VPs of engineering: requests, deletion and transfers: https://safeguard.sh/resources/blog/gdpr-for-vps-of-engineering-requests-deletion-and-transfers?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR Article 32 and Article 28 evidence in the Safeguard compliance suite: https://safeguard.sh/resources/blog/gdpr-article-32-and-article-28-evidence-in-the-safeguard-compliance-suite?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Listen on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03
- YouTubeVideo
Ask Claude "which 5 things do I fix first?" with Safeguard added from the connector directory. Claude reads your Safeguard data, puts known exploited and reachable-with-a-fix findings first, uses severity only to break ties, and batches every vulnerability on one package into on…
Read the full postHide the full post
Ask Claude "which 5 things do I fix first?" with Safeguard added from the connector directory. Claude reads your Safeguard data, puts known exploited and reachable-with-a-fix findings first, uses severity only to break ties, and batches every vulnerability on one package into one upgrade. Read only by default; a person makes the change. Walkthrough: https://na2.hubs.ly/H08Kv0d0 Video: Mixkit stock footage (Mixkit Stock Video Free License). The chat and ranking graphics are illustrations; the vulnerability detail screen is the real Safeguard app. #AppSec #DevSecOps #Shorts
- YouTubeVideo
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received d…
Read the full postHide the full post
On a Friday at ten to five, an email arrives with two lines: send me everything you hold about me, and delete my account. The one month clock started when it landed. Mira and Cal follow that request through a small software company and sit in the reviewer's chair: the received date, who checked identity, which systems were searched, who reviewed the package, and the day the answer went out. They explain the one month deadline in Article 12 and the extension rule, how to confirm who is asking without collecting a passport scan, why logs with IP addresses count, what to do about backups when someone asks for erasure, how to correct data and tell the recipients, what data portability covers, and what a record of processing is for. They also cover the controller and processor question for a company that sells to businesses, and where Safeguard fits on the software evidence side without making anyone compliant. Before that, three stories: the noyb complaints against Scale AI filed on 27 October (allegations, with the company's response), the French regulator's fine against Extia over erasure requests, and the draft EDPB guidelines on fines that are open for comment until 13 November. Theo asks whether your deletion button really deletes, and the episode ends with a checklist for before your window opens. If you run a small software company and need to answer GDPR data subject requests, this episode covers the one month deadline under Article 12, identity checks, the right of access, the right to erasure and backups, rectification, data portability, the record of processing under Article 30, controller and processor roles, and the audit evidence a regulator or customer reviewer asks to see. It also looks at EDPB draft fining guidelines and recent enforcement by the CNIL. Topics: GDPR, data subject access request, DSAR, right to erasure, data portability, record of processing, controller and processor, audit evidence, audit readiness, EDPB, CNIL, noyb, Scale AI, Extia. Chapters: 00:00 Cold open 00:50 Intro 01:25 News: noyb and Scale AI, the Extia fine, the EDPB fining guidelines 05:18 Audit story: the Friday inbox 07:42 Deep dive: the one month clock, access, erasure, backups and the record 14:34 Practitioner corner 15:33 Checklist: before the next request 17:08 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 How to answer a GDPR data subject access request step by step: https://safeguard.sh/resources/blog/how-to-answer-a-gdpr-dsar-step-by-step?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 DSAR export pipeline architecture: https://safeguard.sh/resources/blog/dsar-export-pipeline-architecture?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Verify a requester's identity without collecting more data: https://safeguard.sh/resources/blog/verify-requester-identity-without-collecting-more-data?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Erasure requests and backups: what to do: https://safeguard.sh/resources/blog/erasure-requests-and-backups-what-to-do?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Rectification requests: propagate corrections: https://safeguard.sh/resources/blog/rectification-requests-propagate-corrections?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Data portability, Article 20: export format choices: https://safeguard.sh/resources/blog/data-portability-article-20-export-format-choices?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 The Article 30 record of processing: the engineering view: https://safeguard.sh/resources/blog/ropa-article-30-fields-engineering-view?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Is an IP address in a log personal data?: https://safeguard.sh/resources/blog/is-an-ip-address-in-a-log-personal-data-gdpr?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR for VPs of engineering: requests, deletion and transfers: https://safeguard.sh/resources/blog/gdpr-for-vps-of-engineering-requests-deletion-and-transfers?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 GDPR Article 32 and Article 28 evidence in the Safeguard compliance suite: https://safeguard.sh/resources/blog/gdpr-article-32-and-article-28-evidence-in-the-safeguard-compliance-suite?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03 Listen on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb?utm_source=podcast&utm_medium=video&utm_campaign=the-audit-window&utm_content=ep03
- YouTubeVideo
When a customer or a regulator asks what changed, the answer is a diff between two SBOMs. Generate one per release in CI with safeguard ci scan, gate it, publish an immutable copy in Portal, then compare two releases. Safeguard signs the attestations it produces; signing your ow…
Read the full postHide the full post
When a customer or a regulator asks what changed, the answer is a diff between two SBOMs. Generate one per release in CI with safeguard ci scan, gate it, publish an immutable copy in Portal, then compare two releases. Safeguard signs the attestations it produces; signing your own SBOM file is still your step. Full pipeline: https://na2.hubs.ly/H08Ks3_0 Footage: SBOM explainer animation by the U.S. Department of Homeland Security (public domain, https://na2.hubs.ly/H08Ks5v0). People footage: Mixkit stock (Mixkit Stock Video Free License). #SBOM #DevSecOps #Shorts
 YouTubeVideo
Mellow lo-fi beats for coding, code review and long incident hours. No talk, no ads from us, just focus. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable…
Read the full postHide the full post
Mellow lo-fi beats for coding, code review and long incident hours. No talk, no ads from us, just focus. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardLofi #LofiBeats #FocusMusic #DevSecOps #AppSec #SoftwareSupplyChain
 YouTubeVideo
Short product walkthroughs on a loop, around the clock: generating and managing SBOMs, blocking malicious packages with Package Firewall, scanning your code and containers, and getting fix pull requests that your own CI tests. Watch how Safeguard, the software supply chain secur…
Read the full postHide the full post
Short product walkthroughs on a loop, around the clock: generating and managing SBOMs, blocking malicious packages with Package Firewall, scanning your code and containers, and getting fix pull requests that your own CI tests. Watch how Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams, works in practice. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardDemo #SBOM #PackageFirewall #DevSecOps #AppSec #SoftwareSupplyChain
 YouTubeVideo
Back to back episodes of the Safeguard podcasts, around the clock: Ask Safeguard, The Fix Window, The Audit Window, Patch Monday and Permission Prompt. Practical software supply chain security talk for AppSec, DevSecOps and compliance teams. Safeguard is the software supply chai…
Read the full postHide the full post
Back to back episodes of the Safeguard podcasts, around the clock: Ask Safeguard, The Fix Window, The Audit Window, Patch Monday and Permission Prompt. Practical software supply chain security talk for AppSec, DevSecOps and compliance teams. Safeguard is the software supply chain security platform for those teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardPodcast #AskSafeguard #DevSecOps #AppSec #SoftwareSupplyChain
 YouTubeVideo
A live, always-on feed of newly published CVEs, CISA Known Exploited Vulnerabilities additions and malicious package reports across npm, PyPI and other registries, drawn as animated cards for AppSec and DevSecOps teams. It reports public advisories and sources, it does not claim…
Read the full postHide the full post
A live, always-on feed of newly published CVEs, CISA Known Exploited Vulnerabilities additions and malicious package reports across npm, PyPI and other registries, drawn as animated cards for AppSec and DevSecOps teams. It reports public advisories and sources, it does not claim Safeguard found any of them. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream The cards are generated automatically from public advisory and vulnerability data and rendered as animation. No real people are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. Always check the original advisory before acting. #ThreatRadar #CVE #KEV #SupplyChainSecurity #DevSecOps #AppSec
- YouTubeVideo
Is it safe to auto-merge dependency fixes, and who approves a pull request that a tool wrote? Mira asks the questions teams raise before they let automatic fixes near their repositories, and Cal answers from Safeguard's published docs and posts: the default is a person reviewing…
Read the full postHide the full post
Is it safe to auto-merge dependency fixes, and who approves a pull request that a tool wrote? Mira asks the questions teams raise before they let automatic fixes near their repositories, and Cal answers from Safeguard's published docs and posts: the default is a person reviewing every fix, auto-merge is opt-in and gated behind passing CI, your tests run before a pull request opens, and transitive dependencies are fixed by the smallest change that works, with fork and patch when upstream has no fix. For AppSec leads, DevSecOps teams, platform engineers and engineering managers evaluating autonomous remediation, auto-fix pull requests and AI vulnerability remediation. Topics: automatic fix pull requests, autonomous remediation, auto-merge, dependency updates, transitive dependencies, npm overrides, fork and patch, bulk remediation, CI, human review, reachability, software supply chain security, security podcast, cybersecurity podcast, AppSec podcast, DevSecOps podcast. Chapters: 00:00 Cold open 00:26 Intro 00:48 Question 1: Is it safe to auto-merge dependency fixes? 01:42 Question 2: Who approves and merges a fix pull request? 02:33 Question 3: Does it run my tests before it opens a pull request? 03:22 Question 4: How do I fix a transitive dependency without waiting for the maintainer? 04:16 Question 5: How do I control which fixes apply automatically? 05:09 Question 6: Can I fix many repositories at once? 05:53 Recap and call to action 06:09 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05 Listen on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05
 YouTubeVideo
No talk, no ads from us, just focus. Built by Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate a…
Read the full postHide the full post
No talk, no ads from us, just focus. Built by Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardFM #AmbientMusic #FocusMusic #DevSecOps #AppSec #SoftwareSupplyChain
- YouTubeVideo
US clocks go back this Sunday, 1 November, at 2:00 local time. The IANA time zone database carries that rule to your servers, phones and code, but only when an update ships it. One host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in U…
Read the full postHide the full post
US clocks go back this Sunday, 1 November, at 2:00 local time. The IANA time zone database carries that rule to your servers, phones and code, but only when an update ships it. One host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review jobs scheduled in local time, and list the tzdata version in every image. Footage: NIST (public domain, via Wikimedia Commons), Mixkit stock (free license), local terminal recording, IANA release notes. Walkthrough: https://na2.hubs.ly/H08Ks350 #SRE #DevOps #Shorts
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.