

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on X
RSS feed X
WYSIWYG gave security sameness: one advisory, one patch, everyone covered. Agents build every app to order now (WYGIWYN), so the build is the unit to secure. Eight controls that hold up. https://t.co/eNcCLLAYEl https://t.co/yWvX1SFOfo
 XVideo
Standardised on Anthropic's Claude or OpenAI's ChatGPT? Where your code and prompts go is still your call. Bring your model. Pick where Safeguard runs, SaaS to air-gapped. Air-gapped means Safeguard's or open-weight models. Your model, your call (2/3) https://t.co/w0G95ogBnr htt…
Read the full postHide the full post
Standardised on Anthropic's Claude or OpenAI's ChatGPT? Where your code and prompts go is still your call. Bring your model. Pick where Safeguard runs, SaaS to air-gapped. Air-gapped means Safeguard's or open-weight models. Your model, your call (2/3) https://t.co/w0G95ogBnr https://t.co/QyvQcaaz7k
 X
Security tools stall when the 20th team needs access. Rollout order: pilot one team, SSO + MFA + roles first, policies in Warn, then Block the gates that matter. https://t.co/5bmgr3kV8j https://t.co/HhdHlNvmYt
 X
A skill's description is its trigger, and its scripts are what runs. How to write a https://t.co/1a4Pb2NCYj that loads when it should, plus 8 risks with a control for each, from trojaned scripts to silent updates. https://t.co/vJ23xsHpAa https://t.co/5vM2QFFDXZ
 X
An MCP server is a program with your credentials. The lethal trifecta: private data + untrusted content + a way out. Then all 10 OWASP MCP risks, each with a fix. Includes the postmark-mcp backdoor that BCC'd every email. https://t.co/xcKcG1OElw https://t.co/i5qS5vii0U
 X
XXE keeps coming back because it is mostly parser configuration, not library versions. Fix it where it lands: a CI rule for parser setup plus a negative test with a DOCTYPE fixture. Settings for 7 languages inside. https://t.co/lNw5LhbN0A https://t.co/ZCWasGwF5F
 XVideo
New security rule? Ship it as a warn first. In Safeguard a policy's action is Block, Warn or Notify. Warn passes the gate and names the policy. Fix what it finds, flip to Block, and let CI fail the build on a failed gate. https://t.co/ROgzSuUs71 https://t.co/ypW6fFM5D4
Read the full postHide the full post
New security rule? Ship it as a warn first. In Safeguard a policy's action is Block, Warn or Notify. Warn passes the gate and names the policy. Fix what it finds, flip to Block, and let CI fail the build on a failed gate. https://t.co/ROgzSuUs71 https://t.co/ypW6fFM5D4
 X
A risk acceptance with no expiry date is a finding nobody looks at again. In Safeguard an expired mitigation counts again in gates, with reminders at 14 days, 7 days and on the day. https://t.co/oA7rDjL8tL https://t.co/VBT2TYr2OP
 X
Anthropic's S-1 doubles as an AI vendor review checklist. Ask any model provider: what is retained and where, what can an agent do without approval, what notice before a model is withdrawn, when will you tell us about an incident? 14 questions: https://t.co/7ptMolzrh6 https://t.…
Read the full postHide the full post
Anthropic's S-1 doubles as an AI vendor review checklist. Ask any model provider: what is retained and where, what can an agent do without approval, what notice before a model is withdrawn, when will you tell us about an incident? 14 questions: https://t.co/7ptMolzrh6 https://t.co/NRwLwppm5J
 XVideo
Safeguard Desktop 3.3.0 is out. Electron 45, saved sign-in encrypted with your computer's own key, a sandboxed Linux AppImage. Mac builds signed and notarized, SHA-256 checksums listed. https://t.co/6XVLzIEMJC https://t.co/pTiMCCu7he
 X
How does a small team fix many repos at once? Select the vulnerabilities, run remediation on the selection, get one pull request per repo, and review them. Only the exceptions need a person. https://t.co/IQotVrkXPS https://t.co/0qmVO4jyQx
Read the full postHide the full post
How does a small team fix many repos at once? Select the vulnerabilities, run remediation on the selection, get one pull request per repo, and review them. Only the exceptions need a person. https://t.co/IQotVrkXPS https://t.co/0qmVO4jyQx
 X
A licence change is a supply chain event. Redis 7.2.x and earlier: BSD 3-Clause. 7.4.x to 7.8.x: RSALv2 or SSPLv1. Valkey continues from 7.2.4 under BSD. What does your SBOM say about the Redis-compatible server you run? https://t.co/OR4v3B2P27 https://t.co/65yYmJAlL1
 X
Does an auto-fix run your tests first? With CI connected, yes: your own tests run against the change before the PR opens. A failing build never gets auto-merged. A fix is only as checked as your tests are. https://t.co/9aThACKdyU https://t.co/LjgOa5C5QC
Read the full postHide the full post
Does an auto-fix run your tests first? With CI connected, yes: your own tests run against the change before the PR opens. A failing build never gets auto-merged. A fix is only as checked as your tests are. https://t.co/9aThACKdyU https://t.co/LjgOa5C5QC
 X
New on The Audit Window: GDPR for a small SaaS. One data subject request, one month to answer, and the evidence behind it. https://t.co/WQ2pxmSMHx https://t.co/OwxyXAFFZO
 X
Auto-merge for dependency fixes: safe enough to be a setting, not safe enough to be the default. Opt in, scoped per repo and severity, and only after your own CI passes. https://t.co/4mcmUGVR8n https://t.co/PQZP0QDADs
Read the full postHide the full post
Auto-merge for dependency fixes: safe enough to be a setting, not safe enough to be the default. Opt in, scoped per repo and severity, and only after your own CI passes. https://t.co/4mcmUGVR8n https://t.co/PQZP0QDADs
 X
About USD 6.3 billion left Binance on 29 Oct, most of it in about 20 minutes (TRM Labs). The FBI names North Korea's TraderTraitor; the attack path is not public yet. What is known and a checklist for developer machines: https://t.co/QaQgHrT6sx https://t.co/Vu3BX6jybY
 XVideo
Your agent is about to get a new tool. Who wrote it, and what can it touch? Gold Open Source shows the publisher namespace, version, hosted or installable, and the source repo. Free, no login. Tools and scopes you read yourself in a test client. https://t.co/UP4iT3qXkT https://t…
Read the full postHide the full post
Your agent is about to get a new tool. Who wrote it, and what can it touch? Gold Open Source shows the publisher namespace, version, hosted or installable, and the source repo. Free, no login. Tools and scopes you read yourself in a test client. https://t.co/UP4iT3qXkT https://t.co/QCaZIO32Uk
 X
Safeguard is listed among SCA tools on OWASP's Component Analysis page. A line in a table, not an endorsement. The page is still a solid checklist for testing any SCA tool: inventory, transitive depth, SBOM, VEX, remediation. https://t.co/pIfmPuVTod https://t.co/bO93HP3NZO
 XVideo
The image you are about to push: has anything checked it? A scan job that pulls from a registry runs after the push. Scan in the build job, fail the step on severity, push only what passed. https://t.co/GY5hXNHCt7 https://t.co/EWP4bzamFS
 X
Five scanners, five inboxes, one library reported three times. Safeguard merges duplicates across engines into one finding, ranks by KEV, EPSS and static reachability, and never suppresses what it can't decide. https://t.co/Wqdk16gdlK https://t.co/HtJWGd3Fva
 X
A vendor questionnaire is what they said once. An SBOM, rescanned against new vulnerability data, is what they ship today. Tier vendors, set a cadence per tier, watch a 0 to 100 score. https://t.co/ZaUxJwhWPj https://t.co/jxo3SA7tXX
 X
GitLab CVE-2026-97229, CVSS 10.0. Fixed in 19.4.2, 19.3.5, 19.2.8, but the real fix is in Ruby's Onigmo regex engine. Official packages: check the GitLab version. Own Ruby: check that too. Version commands and runner review: https://t.co/R4WYhHOb12 https://t.co/VBAkLVL3ES
 X
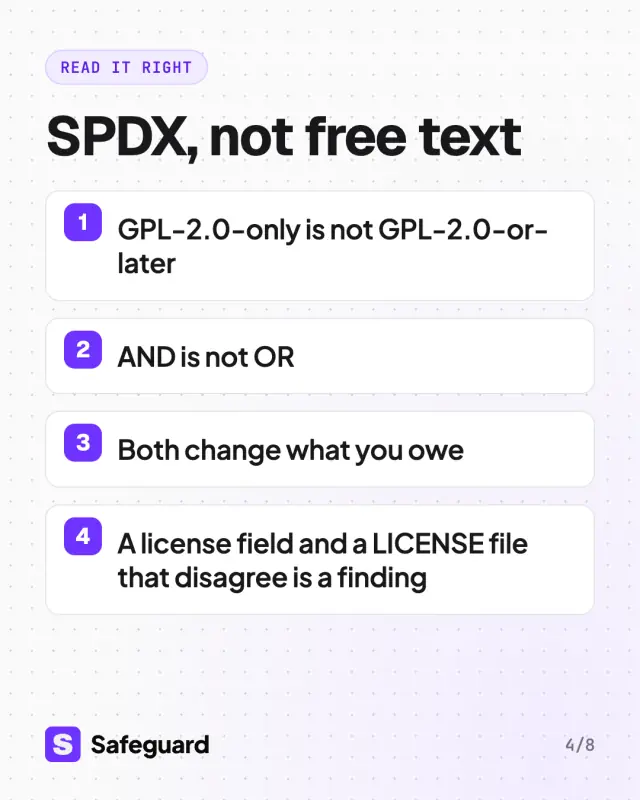
Is there GPL code in this OTA image? Answer it from an inventory with an SPDX license on every line, a policy set before the release, and exceptions with an approver and an expiry date. Not from memory. https://t.co/54GBmqvCYV https://t.co/kjuMIBWUyf
- XVideo
PostgreSQL 14 gets its final release on 12 November. After that, new bugs in 14 get fixed in newer versions only. Find every 14: CI images, migration jobs, replicas, vendor appliances. Then plan the move to 18. https://t.co/0WePzRMO1P https://t.co/KxyMmIrXbF
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.