

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Facebook
Software used to be WYSIWYG: what you see is what you get. With coding agents building every app to order, it is WYGIWYN: what you get is what you need. And no two builds share a supply chain. Here is what security has to do about it: https://na2.hubs.ly/H08Lt-b0
Read the full postHide the full post
Software used to be WYSIWYG: what you see is what you get. With coding agents building every app to order, it is WYGIWYN: what you get is what you need. And no two builds share a supply chain. Here is what security has to do about it: https://na2.hubs.ly/H08Lt-b0
- LinkedIn
For thirty years software was WYSIWYG: what you see is what you get. Millions of teams ran the same release of the same package, so one advisory protected everyone at once. Coding agents break that. They pick the packages, the model, the skills and the connectors for each task,…
Read the full postHide the full post
For thirty years software was WYSIWYG: what you see is what you get. Millions of teams ran the same release of the same package, so one advisory protected everyone at once. Coding agents break that. They pick the packages, the model, the skills and the connectors for each task, so two teams asking for the same service get different trees and different call paths. "Known good" stops being something we share. Our new post argues the unit of security becomes the build: an SBOM and AI-BOM per build, verifiable provenance, static reachability, a policy gate in CI, a package firewall in front of installs, explicit agent permission modes, and fixes that arrive as pull requests your own CI tests. WYGIWYN: what you get is what you need. https://lnkd.in/g5DMxEpG
- Instagram
WYSIWYG is over. Agents now pick your packages, models and skills per task, so no two builds share a supply chain. Our new post covers the eight controls that follow each build. Link in bio: safeguard.sh/resources/blog/from-wysiwyg-to-wygiwyn-what-you-get-is-what-you-need
Read the full postHide the full post
WYSIWYG is over. Agents now pick your packages, models and skills per task, so no two builds share a supply chain. Our new post covers the eight controls that follow each build. Link in bio: safeguard.sh/resources/blog/from-wysiwyg-to-wygiwyn-what-you-get-is-what-you-need
- X
WYSIWYG gave security sameness: one advisory, one patch, everyone covered. Agents build every app to order now (WYGIWYN), so the build is the unit to secure. Eight controls that hold up. https://t.co/eNcCLLAYEl https://t.co/yWvX1SFOfo
 InstagramVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model: Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compa…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model: Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compatible, Anthropic Messages or Gemini API. Then you pick where it runs: SaaS in the US, EU (Frankfurt) or Gov, a private VPC, on-prem, or air-gapped with Safeguard's models inside. Honest note: closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models. Your model, your call (2 of 3). Link in bio: http://safeguard.sh/resources/blog Claude is a product of Anthropic. ChatGPT is a product of OpenAI. #appsec #supplychainsecurity #dataresidency #cybersecurity #devsecops
 Instagram
Most security tools stall when the twentieth team needs access. The fix is order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an org…
Read the full postHide the full post
Most security tools stall when the twentieth team needs access. The fix is order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an org hierarchy and an audit log you can stream to your SIEM. Link in bio: http://safeguard.sh/resources/blog/roll-out-safeguard-across-an-enterprise-sso-scim-roles-org-hierarchy-and-audit-log #SSO #SCIM #AppSec #DevSecOps
 LinkedInVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you make both halves of that call. The model. Claude or GPT models through your own vendor account, Safeguard's own models, a self-hoste…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you make both halves of that call. The model. Claude or GPT models through your own vendor account, Safeguard's own models, a self-hosted or open-weight model, or one you built behind an OpenAI-compatible, Anthropic Messages or Gemini API. An admin adds it under Integrations, Configure Scanner, Models, the key stays in the credential vault, and "Route jobs to this model" sends Safeguard's AI features, such as search and chat, to it. The deployment. Safeguard SaaS in the US, EU (Frankfurt) or Gov region, a private VPC, on-prem, or air-gapped with Safeguard's own models included. One honest note. Closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models. And with Safeguard SaaS, a self-hosted endpoint has to be reachable from Safeguard. Your model, your deployment, your call. (2 of 3 in the series "Your model, your call") Where your code and data go: https://lnkd.in/gnwZMkP4 Claude is a product of Anthropic. ChatGPT is a product of OpenAI. #AppSec #SupplyChainSecurity #DataResidency #CISO
- FacebookVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. With Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-com…
Read the full postHide the full post
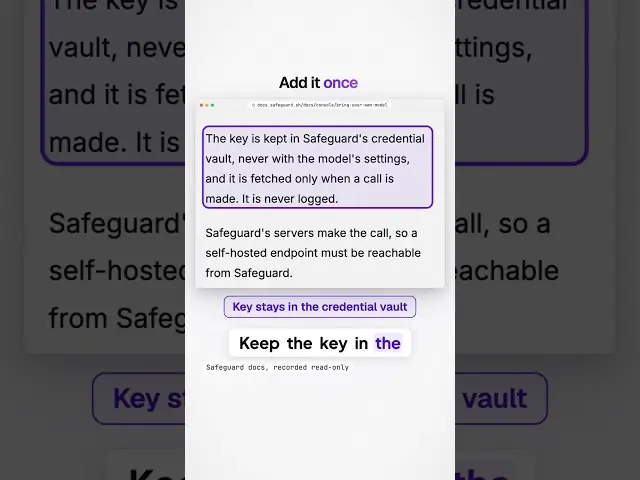
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. With Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compatible, Anthropic Messages or Gemini API) and where it runs (SaaS in the US, EU (Frankfurt) or Gov, a private VPC, on-prem, or air-gapped with Safeguard's models inside). Honest note: closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models, and a self-hosted endpoint must be reachable from Safeguard SaaS. Your model, your call (2/3). Where your code and data go: https://na2.hubs.ly/H08FzbF0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI.
 YouTubeVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compa…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. In Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compatible, Anthropic Messages or Gemini API) and where it runs (SaaS in the US, EU (Frankfurt) or Gov, a private VPC, on-prem, or air-gapped with Safeguard's models inside). Honest note: closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models, and a self-hosted endpoint must be reachable from Safeguard SaaS. Where your code and data go: https://na2.hubs.ly/H08FzbG0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI. Stock footage: Mixkit (Mixkit Stock Video Free License). Product footage: Safeguard docs, recorded read-only. #appsec #supplychainsecurity #dataresidency
- Facebook
Most security tools stall when the twentieth team needs access. Our rollout order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an or…
Read the full postHide the full post
Most security tools stall when the twentieth team needs access. Our rollout order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an org hierarchy and an audit log you can stream to your SIEM: https://na2.hubs.ly/H08J5jW0
- LinkedIn
Most security tools stall after the first enthusiastic team, when the twentieth team needs access. The blockers are about identity and control, not scanning. A rollout order that works: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, the…
Read the full postHide the full post
Most security tools stall after the first enthusiastic team, when the twentieth team needs access. The blockers are about identity and control, not scanning. A rollout order that works: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. The pieces it leans on: SAML 2.0 or OpenID Connect sign-in, SCIM 2.0 deprovisioning, built-in and custom roles scoped to an organization or team, a tenant and organization hierarchy, and an append-only audit log you can stream to your SIEM. The full guide for the AppSec or platform owner running the rollout and the identity architect signing it off: https://lnkd.in/gnwzBv5A #SSO #SCIM #AppSec #DevSecOps
- XVideo
Standardised on Anthropic's Claude or OpenAI's ChatGPT? Where your code and prompts go is still your call. Bring your model. Pick where Safeguard runs, SaaS to air-gapped. Air-gapped means Safeguard's or open-weight models. Your model, your call (2/3) https://t.co/w0G95ogBnr htt…
Read the full postHide the full post
Standardised on Anthropic's Claude or OpenAI's ChatGPT? Where your code and prompts go is still your call. Bring your model. Pick where Safeguard runs, SaaS to air-gapped. Air-gapped means Safeguard's or open-weight models. Your model, your call (2/3) https://t.co/w0G95ogBnr https://t.co/QyvQcaaz7k
- X
Security tools stall when the 20th team needs access. Rollout order: pilot one team, SSO + MFA + roles first, policies in Warn, then Block the gates that matter. https://t.co/5bmgr3kV8j https://t.co/HhdHlNvmYt
- TikTokVideo
On Claude or ChatGPT? Where your code goes is still your call. Bring your model, pick where Safeguard runs: US, EU (Frankfurt), Gov, VPC, on-prem, air-gapped. Closed models never run on-prem or air-gapped, so air-gapped = Safeguard's or open-weight models. Your model, your call…
Read the full postHide the full post
On Claude or ChatGPT? Where your code goes is still your call. Bring your model, pick where Safeguard runs: US, EU (Frankfurt), Gov, VPC, on-prem, air-gapped. Closed models never run on-prem or air-gapped, so air-gapped = Safeguard's or open-weight models. Your model, your call 2/3. Claude is a product of Anthropic. ChatGPT is a product of OpenAI. #appsec #supplychainsecurity #dataresidency
 Instagram
A skill is a folder, not a prompt. The description loads first, the scripts run later, and nobody reads them in between. Our new guide shows how to write and test a http://SKILL.md, then the eight risks and a control for each. Link in bio: safeguard.sh/resources/blog/how-to-writ…
Read the full postHide the full post
A skill is a folder, not a prompt. The description loads first, the scripts run later, and nobody reads them in between. Our new guide shows how to write and test a http://SKILL.md, then the eight risks and a control for each. Link in bio: safeguard.sh/resources/blog/how-to-write-and-secure-agent-skills-skill-md-authoring-testing-permissions-and-supply-chain-controls
- LinkedIn
Writing an Agent Skill takes ten minutes. Writing one that triggers on the right requests and does not hand an attacker your shell takes real engineering. A skill is a folder with a https://lnkd.in/gZ44vq46, loaded in stages: the description first, the body when a task matches,…
Read the full postHide the full post
Writing an Agent Skill takes ten minutes. Writing one that triggers on the right requests and does not hand an attacker your shell takes real engineering. A skill is a folder with a https://lnkd.in/gZ44vq46, loaded in stages: the description first, the body when a task matches, bundled files only when the instructions call for them. That is why the parts that run are the parts nobody reads until they run. Our new guide goes field by field through the format, shows how to write and test a skill so the description triggers it, then takes apart eight risks with a control for each: trojaned scripts, injected instructions, broad allowed tools, inline shell, secrets, impersonated marketplaces, runtime installs and silent updates. https://lnkd.in/gjnyYWBk
- Facebook
Agent Skills are easy to write and easy to under review. Here is how to write a https://na2.hubs.ly/H08LsLS0 that triggers correctly, and the eight risks to check before you install or share one: https://na2.hubs.ly/H08LsLV0
Read the full postHide the full post
Agent Skills are easy to write and easy to under review. Here is how to write a https://na2.hubs.ly/H08LsLS0 that triggers correctly, and the eight risks to check before you install or share one: https://na2.hubs.ly/H08LsLV0
- X
A skill's description is its trigger, and its scripts are what runs. How to write a https://t.co/1a4Pb2NCYj that loads when it should, plus 8 risks with a control for each, from trojaned scripts to silent updates. https://t.co/vJ23xsHpAa https://t.co/5vM2QFFDXZ
 Instagram
Every MCP server you connect is code running with your credentials. Our new guide covers the OWASP MCP Top 10, the lethal trifecta, and a fix for each of the ten risks, from tool poisoning to shadow servers. Link in bio: safeguard.sh/resources/blog/what-is-an-mcp-server-and-how-…
Read the full postHide the full post
Every MCP server you connect is code running with your credentials. Our new guide covers the OWASP MCP Top 10, the lethal trifecta, and a fix for each of the ten risks, from tool poisoning to shadow servers. Link in bio: safeguard.sh/resources/blog/what-is-an-mcp-server-and-how-to-secure-it-owasp-mcp-top-10-explained
- Facebook
Which MCP servers are your AI assistants connected to, and who approved them? The OWASP MCP Top 10 explained in plain terms, with a fix for every risk, from leaked tokens to shadow servers: https://na2.hubs.ly/H08LsLc0
Read the full postHide the full post
Which MCP servers are your AI assistants connected to, and who approved them? The OWASP MCP Top 10 explained in plain terms, with a fix for every risk, from leaked tokens to shadow servers: https://na2.hubs.ly/H08LsLc0
- LinkedIn
An MCP server is code you run with your credentials. Most teams approve one and never look again. On 25 September 2025 Postmark said someone had impersonated it with an npm package called postmark-mcp. After 15 clean versions, 1.0.16 quietly blind copied every email the tool sen…
Read the full postHide the full post
An MCP server is code you run with your credentials. Most teams approve one and never look again. On 25 September 2025 Postmark said someone had impersonated it with an npm package called postmark-mcp. After 15 clean versions, 1.0.16 quietly blind copied every email the tool sent to an outside address. Nothing in the tool description changed, so neither the model nor the user could see it. Our new guide explains MCP at the wire level, then the lethal trifecta (private data, untrusted content and a way out), then all ten OWASP MCP Top 10 risks with a concrete fix for each, from token leaks and tool poisoning to shadow servers. It also notes the OWASP list is still in beta, so treat it as an evolving reference. https://lnkd.in/g3C4rGKk
- X
An MCP server is a program with your credentials. The lethal trifecta: private data + untrusted content + a way out. Then all 10 OWASP MCP risks, each with a fix. Includes the postmark-mcp backdoor that BCC'd every email. https://t.co/xcKcG1OElw https://t.co/i5qS5vii0U
 Facebook
Fixed an XXE finding and it came back? A new parser with default settings probably shipped in a new place. Parser settings for Java, .NET, Python, PHP, Go, http://Node.js and Ruby, plus the CI checks that stop an unsafe parser from merging: https://na2.hubs.ly/H08Lrsc0
Read the full postHide the full post
Fixed an XXE finding and it came back? A new parser with default settings probably shipped in a new place. Parser settings for Java, .NET, Python, PHP, Go, http://Node.js and Ruby, plus the CI checks that stop an unsafe parser from merging: https://na2.hubs.ly/H08Lrsc0
- LinkedIn
You fixed an XXE finding by hand. Months later it is back. XXE is mostly a configuration problem, not a library version problem. A SAML handler, an SVG preview or a partner feed reader arrives with a one line parse call, and nothing tells its author about the setting the other p…
Read the full postHide the full post
You fixed an XXE finding by hand. Months later it is back. XXE is mostly a configuration problem, not a library version problem. A SAML handler, an SVG preview or a partner feed reader arrives with a one line parse call, and nothing tells its author about the setting the other parsers have. Our new post makes it a pull request check. It covers the parser settings for Java, .NET, Python, PHP, Go, http://Node.js and Ruby, then three CI checks: a static rule for parser construction, a negative test with a DOCTYPE fixture the parser must reject, and runtime version assertions. It also lists library versions with XXE fixes, such as lxml 6.1.0 and Nokogiri 1.19.4, and notes that some advisories have no patched version at all. https://lnkd.in/gQUdsKQm
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.