

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on Facebook
RSS feed Facebook
Software used to be WYSIWYG: what you see is what you get. With coding agents building every app to order, it is WYGIWYN: what you get is what you need. And no two builds share a supply chain. Here is what security has to do about it: https://na2.hubs.ly/H08Lt-b0
Read the full postHide the full post
Software used to be WYSIWYG: what you see is what you get. With coding agents building every app to order, it is WYGIWYN: what you get is what you need. And no two builds share a supply chain. Here is what security has to do about it: https://na2.hubs.ly/H08Lt-b0
 FacebookVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. With Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-com…
Read the full postHide the full post
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, where your code and prompts go should be your decision. With Safeguard you pick the model (Claude or GPT models through your own vendor account, Safeguard's own models, or one you host behind an OpenAI-compatible, Anthropic Messages or Gemini API) and where it runs (SaaS in the US, EU (Frankfurt) or Gov, a private VPC, on-prem, or air-gapped with Safeguard's models inside). Honest note: closed models from Anthropic, OpenAI, Google and xAI never run on-prem or air-gapped, so air-gapped means Safeguard's or open-weight models, and a self-hosted endpoint must be reachable from Safeguard SaaS. Your model, your call (2/3). Where your code and data go: https://na2.hubs.ly/H08FzbF0 Claude is a product of Anthropic. ChatGPT is a product of OpenAI.
 Facebook
Most security tools stall when the twentieth team needs access. Our rollout order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an or…
Read the full postHide the full post
Most security tools stall when the twentieth team needs access. Our rollout order: pilot one team, put SSO, multi-factor and roles in first, run policies in Warn or Notify, then switch the gates that matter to Block. SAML or OIDC sign-in, SCIM deprovisioning, scoped roles, an org hierarchy and an audit log you can stream to your SIEM: https://na2.hubs.ly/H08J5jW0
 Facebook
Agent Skills are easy to write and easy to under review. Here is how to write a https://na2.hubs.ly/H08LsLS0 that triggers correctly, and the eight risks to check before you install or share one: https://na2.hubs.ly/H08LsLV0
Read the full postHide the full post
Agent Skills are easy to write and easy to under review. Here is how to write a https://na2.hubs.ly/H08LsLS0 that triggers correctly, and the eight risks to check before you install or share one: https://na2.hubs.ly/H08LsLV0
 Facebook
Which MCP servers are your AI assistants connected to, and who approved them? The OWASP MCP Top 10 explained in plain terms, with a fix for every risk, from leaked tokens to shadow servers: https://na2.hubs.ly/H08LsLc0
Read the full postHide the full post
Which MCP servers are your AI assistants connected to, and who approved them? The OWASP MCP Top 10 explained in plain terms, with a fix for every risk, from leaked tokens to shadow servers: https://na2.hubs.ly/H08LsLc0
 Facebook
Fixed an XXE finding and it came back? A new parser with default settings probably shipped in a new place. Parser settings for Java, .NET, Python, PHP, Go, http://Node.js and Ruby, plus the CI checks that stop an unsafe parser from merging: https://na2.hubs.ly/H08Lrsc0
Read the full postHide the full post
Fixed an XXE finding and it came back? A new parser with default settings probably shipped in a new place. Parser settings for Java, .NET, Python, PHP, Go, http://Node.js and Ruby, plus the CI checks that stop an unsafe parser from merging: https://na2.hubs.ly/H08Lrsc0
 FacebookVideo
A new blocking rule that breaks every build tends to get switched off. In Safeguard a policy's action is Block, Warn or Notify. Start the rule as a warn (the gate passes and names the policy), fix what it finds, then flip the same rule to Block. In CI, safeguard ci scan --wait -…
Read the full postHide the full post
A new blocking rule that breaks every build tends to get switched off. In Safeguard a policy's action is Block, Warn or Notify. Start the rule as a warn (the gate passes and names the policy), fix what it finds, then flip the same rule to Block. In CI, safeguard ci scan --wait --fail-on-gate exits nonzero when the gate fails. Policies vs gates vs guardrails, and where each runs: https://na2.hubs.ly/H08LgP50
 Facebook
"We will fix it later" is fine. "We will fix it later" with no owner and no end date is what fails an audit. How to record a risk acceptance in Safeguard with an approver, evidence and an expiry, and what changes when it runs out: https://na2.hubs.ly/H08LrsQ0
Read the full postHide the full post
"We will fix it later" is fine. "We will fix it later" with no owner and no end date is what fails an audit. How to record a risk acceptance in Safeguard with an approver, evidence and an expiry, and what changes when it runs out: https://na2.hubs.ly/H08LrsQ0
 Facebook
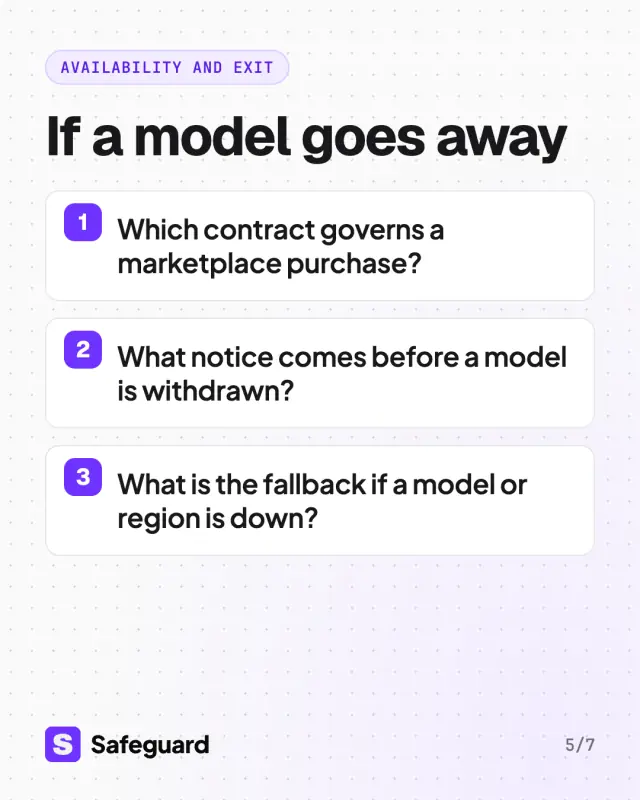
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, it is a handy source of questions for your AI vendor review: what is retained and where, what an agent can do without approval, what notice you get before a model is withdrawn, and how fast you hear about…
Read the full postHide the full post
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, it is a handy source of questions for your AI vendor review: what is retained and where, what an agent can do without approval, what notice you get before a model is withdrawn, and how fast you hear about an incident. Swipe for the questions by group. All 14, mapped to the filing: https://na2.hubs.ly/H08DVgd0 Not investment advice.
 FacebookVideo
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. Mac builds are signed and notarized; Windows and Linux installers list SHA-256…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. Mac builds are signed and notarized; Windows and Linux installers list SHA-256 checksums so you can verify the download. Download: https://na2.hubs.ly/H08LgJS0
 Facebook
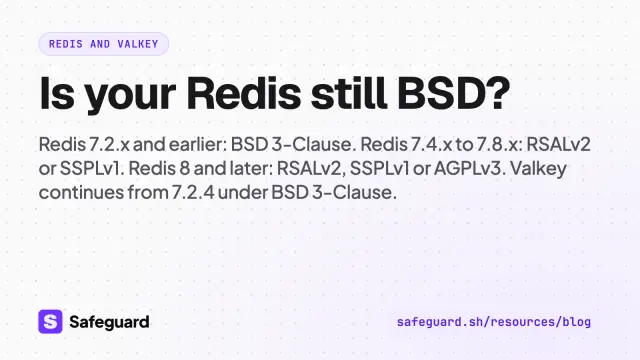
A licence change is a supply chain event. Redis 7.2.x and earlier are BSD 3-Clause. Redis 7.4.x to 7.8.x are RSALv2 or SSPLv1. Redis 8 and later are tri-licensed: RSALv2, SSPLv1 or AGPLv3. Valkey continues from Redis 7.2.4 under BSD 3-Clause. Check what your SBOM says about the…
Read the full postHide the full post
A licence change is a supply chain event. Redis 7.2.x and earlier are BSD 3-Clause. Redis 7.4.x to 7.8.x are RSALv2 or SSPLv1. Redis 8 and later are tri-licensed: RSALv2, SSPLv1 or AGPLv3. Valkey continues from Redis 7.2.4 under BSD 3-Clause. Check what your SBOM says about the Redis-compatible server you run. Not legal advice. Release history and licence by version: https://na2.hubs.ly/H08CLVh0
 Facebook
How does a small team fix many repositories at once? Select the vulnerabilities, run remediation on the selection, and review one pull request per repository instead of a stream of tiny ones. Quick answer: https://na2.hubs.ly/H08Lk_Y0 Full episode: https://na2.hubs.ly/H08Lk_-0
Read the full postHide the full post
How does a small team fix many repositories at once? Select the vulnerabilities, run remediation on the selection, and review one pull request per repository instead of a stream of tiny ones. Quick answer: https://na2.hubs.ly/H08Lk_Y0 Full episode: https://na2.hubs.ly/H08Lk_-0
 Facebook
Does an auto-fix run your tests first? With CI connected, your existing tests run against the proposed change before the pull request opens, and auto-merge never goes past a failing build. Quick answer: https://na2.hubs.ly/H08Lk_h0 Full episode: https://na2.hubs.ly/H08Lk_k0
Read the full postHide the full post
Does an auto-fix run your tests first? With CI connected, your existing tests run against the proposed change before the pull request opens, and auto-merge never goes past a failing build. Quick answer: https://na2.hubs.ly/H08Lk_h0 Full episode: https://na2.hubs.ly/H08Lk_k0
 Facebook
New episode of The Audit Window: GDPR for a small SaaS. One data subject request, one month to answer, and the evidence a reviewer will ask to see. About 18 minutes. Listen on Spotify: https://na2.hubs.ly/H08Lbhv0
Read the full postHide the full post
New episode of The Audit Window: GDPR for a small SaaS. One data subject request, one month to answer, and the evidence a reviewer will ask to see. About 18 minutes. Listen on Spotify: https://na2.hubs.ly/H08Lbhv0
 Facebook
About USD 6.3 billion left Binance on 29 October, most of it in about 20 minutes per TRM Labs. Binance says it may have started with a compromised DevOps laptop, and the FBI names North Korea's TraderTraitor. The full attack path is not public yet. Here is what is known and a fi…
Read the full postHide the full post
About USD 6.3 billion left Binance on 29 October, most of it in about 20 minutes per TRM Labs. Binance says it may have started with a compromised DevOps laptop, and the FBI names North Korea's TraderTraitor. The full attack path is not public yet. Here is what is known and a five-point checklist for developer machines. https://na2.hubs.ly/H08LkX50
 Facebook
Should you auto-merge dependency fixes? Our answer: it should be a setting you turn on, not the default. A person reviews every fix first, and auto-merge only fires after your own tests pass. Short answer here: https://na2.hubs.ly/H08Lk-y0 Full episode: https://na2.hubs.ly/H08Lk…
Read the full postHide the full post
Should you auto-merge dependency fixes? Our answer: it should be a setting you turn on, not the default. A person reviews every fix first, and auto-merge only fires after your own tests pass. Short answer here: https://na2.hubs.ly/H08Lk-y0 Full episode: https://na2.hubs.ly/H08LkZG0
 FacebookVideo
Your agent is about to get a new tool. Who wrote it, and what can it touch? Look the MCP server up first on Gold Open Source (https://na2.hubs.ly/H08LgD30), free with no login. You see the publisher namespace, the version, hosted endpoint or installable package, and the source r…
Read the full postHide the full post
Your agent is about to get a new tool. Who wrote it, and what can it touch? Look the MCP server up first on Gold Open Source (https://na2.hubs.ly/H08LgD30), free with no login. You see the publisher namespace, the version, hosted endpoint or installable package, and the source repository. A package means their code runs on your machine, so check what it depends on. Gold does not list tools or scopes, so read those yourself in a test client. https://na2.hubs.ly/H08Lgz30
 Facebook
Safeguard is now listed among SCA tools on OWASP's Component Analysis page. It is a line in a table, not an endorsement: OWASP says it does not endorse commercial products. The page itself is a good checklist for evaluating any SCA tool. Our post turns it into a test plan: https…
Read the full postHide the full post
Safeguard is now listed among SCA tools on OWASP's Component Analysis page. It is a line in a table, not an endorsement: OWASP says it does not endorse commercial products. The page itself is a good checklist for evaluating any SCA tool. Our post turns it into a test plan: https://na2.hubs.ly/H08J5gS0
 FacebookVideo
The image you are about to push. Has anything checked it yet? A scan in a separate job pulls from a registry, so the image is already pushed. Scan in the build job instead: the Safeguard CLI reads the local image, checks OS packages, the base image and app dependencies, and only…
Read the full postHide the full post
The image you are about to push. Has anything checked it yet? A scan in a separate job pulls from a registry, so the image is already pushed. Scan in the build job instead: the Safeguard CLI reads the local image, checks OS packages, the base image and app dependencies, and only results leave the runner. Fail the step on a severity, push only what passed, and scan again at deploy. Full guide: https://na2.hubs.ly/H08LgsC0 People footage: Mixkit stock (Mixkit Stock Video Free License).
 Facebook
Five scanners, five inboxes, one vulnerable library reported three times. Safeguard puts SCA, SAST, DAST, container and IaC findings in one queue, merges duplicates, ranks by risk and routes each to an owner. Anything it cannot decide on is treated as potentially reachable, neve…
Read the full postHide the full post
Five scanners, five inboxes, one vulnerable library reported three times. Safeguard puts SCA, SAST, DAST, container and IaC findings in one queue, merges duplicates, ranks by risk and routes each to an owner. Anything it cannot decide on is treated as potentially reachable, never suppressed. https://na2.hubs.ly/H08J3Mm0
 Facebook
A yearly vendor questionnaire is a snapshot. Software changes every release. Tier your vendors by criticality, request SBOMs on a cadence per tier, read a 0 to 100 risk score and get alerts when something changes. Here is how Safeguard's Third Party Risk Manager does it. https:/…
Read the full postHide the full post
A yearly vendor questionnaire is a snapshot. Software changes every release. Tier your vendors by criticality, request SBOMs on a cadence per tier, read a 0 to 100 risk score and get alerts when something changes. Here is how Safeguard's Third Party Risk Manager does it. https://na2.hubs.ly/H08LgbJ0
 Facebook
Running self-hosted GitLab? CVE-2026-97229 (CVSS 10.0, CI regex flaw) is fixed in 19.4.2, 19.3.5 and 19.2.8, but the real fix lives in the Ruby underneath. Here is how to check your GitLab and Ruby versions, upgrade, and review CI runner exposure. https://na2.hubs.ly/H08Lgdj0
Read the full postHide the full post
Running self-hosted GitLab? CVE-2026-97229 (CVSS 10.0, CI regex flaw) is fixed in 19.4.2, 19.3.5 and 19.2.8, but the real fix lives in the Ruby underneath. Here is how to check your GitLab and Ruby versions, upgrade, and review CI runner exposure. https://na2.hubs.ly/H08Lgdj0
 Facebook
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and a reco…
Read the full postHide the full post
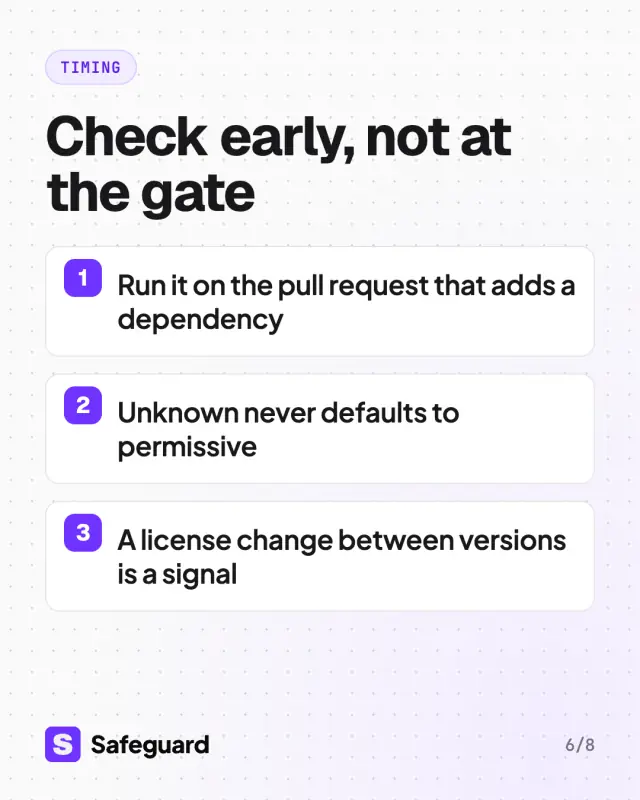
Is there GPL code in this OTA image? Answer it from an inventory with a license on every line, not from memory. Swipe for the routine: one inventory per release version, SPDX identifiers, a policy set before the release, exceptions with an approver and an expiry date, and a record kept with the release. Not legal advice. Full workflow: https://na2.hubs.ly/H08Kyyt0
- FacebookVideo
PostgreSQL 14 gets its final release on 12 November. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run, including CI containers, migration jobs, replicas and vendor appliances, apply the final 14 release when it ships, then plan the move to…
Read the full postHide the full post
PostgreSQL 14 gets its final release on 12 November. After that, new bugs found in 14 get fixed in newer versions only. Find every 14 you run, including CI containers, migration jobs, replicas and vendor appliances, apply the final 14 release when it ships, then plan the move to 18. If you hold SBOMs, a search by package and version lists every project and image that carries it. Write-up: https://na2.hubs.ly/H08LcSW0 Video: Malcolm McLean, PostgresConf South Africa 2018, CC BY 4.0. Stock: Mixkit.
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.