

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Instagram
XXE is mostly a settings problem. Every new SAML handler, SVG preview or SOAP client is a chance to ship a parser with defaults that allow DTDs. Our new post gives you the settings for 7 languages, three CI checks including a DOCTYPE negative test, and the library versions that…
Read the full postHide the full post
XXE is mostly a settings problem. Every new SAML handler, SVG preview or SOAP client is a chance to ship a parser with defaults that allow DTDs. Our new post gives you the settings for 7 languages, three CI checks including a DOCTYPE negative test, and the library versions that fix known XXE bugs. Link in bio: safeguard.sh/resources/blog/stop-xxe-before-merge-parser-settings-ci-checks-and-upgrades
- X
XXE keeps coming back because it is mostly parser configuration, not library versions. Fix it where it lands: a CI rule for parser setup plus a negative test with a DOCTYPE fixture. Settings for 7 languages inside. https://t.co/lNw5LhbN0A https://t.co/ZCWasGwF5F
 LinkedInVideo
A new blocking rule that breaks every build tends to get switched off. Roll it out in two steps instead. In Safeguard, each policy has one action: Block, Warn or Notify. Warn: the gate still passes, with a warning that names the policy. Notify: the gate passes and your channels…
Read the full postHide the full post
A new blocking rule that breaks every build tends to get switched off. Roll it out in two steps instead. In Safeguard, each policy has one action: Block, Warn or Notify. Warn: the gate still passes, with a warning that names the policy. Notify: the gate passes and your channels are told. Block: the gate fails. Start the rule as a warn, watch what it matches, fix what you can, then flip the same rule to Block. A gate with any failing Block policy fails. In CI, one step connects the verdict to your pipeline: safeguard ci scan --wait --fail-on-gate . Per the docs it exits 0 when the gate is Passed or Warning, and nonzero when it is Failed, Error or Not evaluated. Warn early where a fix is cheap, block late where the decision is final. What policies, gates and guardrails each do, and where each runs: https://lnkd.in/g6TpkM9W The five points between editor and cluster where this pays off: https://lnkd.in/gpgUhFQj #DevSecOps #AppSec #SupplyChainSecurity
 InstagramVideo
A new blocking rule that breaks every build gets switched off. Start it as a warn: the gate passes and names the policy. Fix what it finds, flip the same rule to Block, and let CI fail the build on a failed gate. Link in bio: http://safeguard.sh/resources/blog #devsecops #appsec…
Read the full postHide the full post
A new blocking rule that breaks every build gets switched off. Start it as a warn: the gate passes and names the policy. Fix what it finds, flip the same rule to Block, and let CI fail the build on a failed gate. Link in bio: http://safeguard.sh/resources/blog #devsecops #appsec #supplychainsecurity #cicd
- FacebookVideo
A new blocking rule that breaks every build tends to get switched off. In Safeguard a policy's action is Block, Warn or Notify. Start the rule as a warn (the gate passes and names the policy), fix what it finds, then flip the same rule to Block. In CI, safeguard ci scan --wait -…
Read the full postHide the full post
A new blocking rule that breaks every build tends to get switched off. In Safeguard a policy's action is Block, Warn or Notify. Start the rule as a warn (the gate passes and names the policy), fix what it finds, then flip the same rule to Block. In CI, safeguard ci scan --wait --fail-on-gate exits nonzero when the gate fails. Policies vs gates vs guardrails, and where each runs: https://na2.hubs.ly/H08LgP50
 YouTubeVideo
A new blocking rule that breaks every build tends to get switched off. In Safeguard each policy has one action: Block, Warn or Notify. A warn lets the gate pass and names the policy. Fix what it finds, flip the same rule to Block, and let one CI step fail the build when the gate…
Read the full postHide the full post
A new blocking rule that breaks every build tends to get switched off. In Safeguard each policy has one action: Block, Warn or Notify. A warn lets the gate pass and names the policy. Fix what it finds, flip the same rule to Block, and let one CI step fail the build when the gate fails. Footage: Mixkit stock (free license), Safeguard app gates view (our own recording). Policies vs gates vs guardrails: https://na2.hubs.ly/H08LgPc0 #DevSecOps #AppSec #Shorts
- XVideo
New security rule? Ship it as a warn first. In Safeguard a policy's action is Block, Warn or Notify. Warn passes the gate and names the policy. Fix what it finds, flip to Block, and let CI fail the build on a failed gate. https://t.co/ROgzSuUs71 https://t.co/ypW6fFM5D4
Read the full postHide the full post
New security rule? Ship it as a warn first. In Safeguard a policy's action is Block, Warn or Notify. Warn passes the gate and names the policy. Fix what it finds, flip to Block, and let CI fail the build on a failed gate. https://t.co/ROgzSuUs71 https://t.co/ypW6fFM5D4
- TikTokVideo
Start a new security rule as a warn, fix what it finds, then flip it to block. The gate decides what ships. Link in bio: https://na2.hubs.ly/H08LgPd0 #devsecops #appsec #cicd
 Instagram
"We will fix it later" only holds up if someone decided it, wrote down why, and set an end date. Our new post covers the four mitigation types in Safeguard, expiry presets of 30, 90, 180 and 365 days, reminders before it lapses, and the history that serves as your audit trail. E…
Read the full postHide the full post
"We will fix it later" only holds up if someone decided it, wrote down why, and set an end date. Our new post covers the four mitigation types in Safeguard, expiry presets of 30, 90, 180 and 365 days, reminders before it lapses, and the history that serves as your audit trail. Expired means the finding counts again. Link in bio: safeguard.sh/resources/blog/document-a-vulnerability-mitigation-in-safeguard-risk-acceptance-expiry-review-and-audit-trail
- Facebook
"We will fix it later" is fine. "We will fix it later" with no owner and no end date is what fails an audit. How to record a risk acceptance in Safeguard with an approver, evidence and an expiry, and what changes when it runs out: https://na2.hubs.ly/H08LrsQ0
Read the full postHide the full post
"We will fix it later" is fine. "We will fix it later" with no owner and no end date is what fails an audit. How to record a risk acceptance in Safeguard with an approver, evidence and an expiry, and what changes when it runs out: https://na2.hubs.ly/H08LrsQ0
- LinkedIn
Audits rarely fail on the open finding. They fail on the open finding with no record. The record has to answer four questions: who decided, on what basis, when does it end, and has anything changed since. Our new post walks through Mitigations in Safeguard. Four types, each maki…
Read the full postHide the full post
Audits rarely fail on the open finding. They fail on the open finding with no record. The record has to answer four questions: who decided, on what basis, when does it end, and has anything changed since. Our new post walks through Mitigations in Safeguard. Four types, each making a different claim: Risk Acceptance, False Positive, Workaround Applied and Not Applicable. Each carries a justification, an approver, optional evidence and a scope. Expiry is optional in the form, so we argue for making it mandatory in your process. Presets are 30, 90, 180 and 365 days, with reminders 14 days before, 7 days before and on the day. Once it expires, the finding counts again in gates. The History tab and the Mitigations report give you the audit trail. https://lnkd.in/g5jCFeqH
- X
A risk acceptance with no expiry date is a finding nobody looks at again. In Safeguard an expired mitigation counts again in gates, with reminders at 14 days, 7 days and on the day. https://t.co/oA7rDjL8tL https://t.co/VBT2TYr2OP
 Instagram
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, use it to sharpen your AI vendor questionnaire. Swipe for the questions by group: data retention, supply chain, agents and connectors, availability, incidents. All 14 are in the post. Not investment advic…
Read the full postHide the full post
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, use it to sharpen your AI vendor questionnaire. Swipe for the questions by group: data retention, supply chain, agents and connectors, availability, incidents. All 14 are in the post. Not investment advice. Link in bio: http://safeguard.sh/resources/blog/anthropic-s-1-ai-vendor-risk-security-teams #AISecurity #VendorRisk #ThirdPartyRisk #AppSec
- Facebook
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, it is a handy source of questions for your AI vendor review: what is retained and where, what an agent can do without approval, what notice you get before a model is withdrawn, and how fast you hear about…
Read the full postHide the full post
Anthropic filed an S-1 on 26 October 2026. If your team depends on Claude, it is a handy source of questions for your AI vendor review: what is retained and where, what an agent can do without approval, what notice you get before a model is withdrawn, and how fast you hear about an incident. Swipe for the questions by group. All 14, mapped to the filing: https://na2.hubs.ly/H08DVgd0 Not investment advice.
 LinkedIn
Anthropic filed a Form S-1 on 26 October 2026. If your team depends on Claude, the filing is also a source of vendor review questions. It is a preliminary prospectus, so treat it as a dated snapshot. What it gives a security team is a plain account of how a frontier model provid…
Read the full postHide the full post
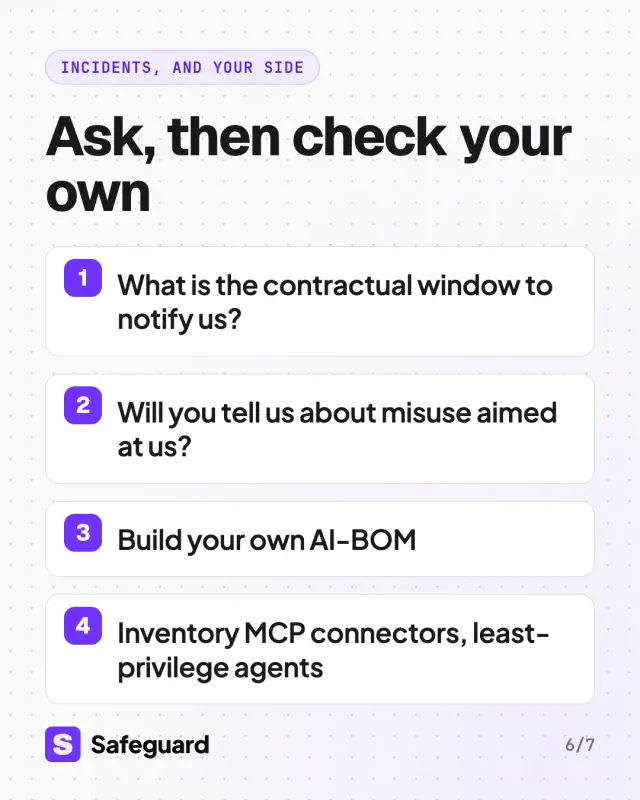
Anthropic filed a Form S-1 on 26 October 2026. If your team depends on Claude, the filing is also a source of vendor review questions. It is a preliminary prospectus, so treat it as a dated snapshot. What it gives a security team is a plain account of how a frontier model provider describes its own risks: weight theft, agent attack paths, cloud concentration, export curbs and incident duties. A sample of the 14 questions in the post: 1. Data: what is retained, for how long, where, and who can access it? 2. Supply chain: do you publish SBOMs for SDKs, CLIs and plugins, and how are releases signed? 3. Agents: what can an agent do without human approval, and how are MCP credentials scoped and revoked? 4. Availability: what notice do we get before a model is restricted or withdrawn? 5. Incidents: what is the contractual window to tell us, and will you tell us about misuse that targeted us? None of these can be answered with a link to a marketing page. Your side counts too: the filing notes that incidents can come from customer misconfiguration, so build an AI-BOM, inventory your MCP connectors and set least-privilege agent permissions. Swipe for the questions by group. Full post, with the mapping from disclosure to question: https://lnkd.in/gDyff7Bk Not investment advice. We read the filing only for what it tells a customer's security team. #AISecurity #VendorRisk #ThirdPartyRisk
 X
Anthropic's S-1 doubles as an AI vendor review checklist. Ask any model provider: what is retained and where, what can an agent do without approval, what notice before a model is withdrawn, when will you tell us about an incident? 14 questions: https://t.co/7ptMolzrh6 https://t.…
Read the full postHide the full post
Anthropic's S-1 doubles as an AI vendor review checklist. Ask any model provider: what is retained and where, what can an agent do without approval, what notice before a model is withdrawn, when will you tell us about an incident? 14 questions: https://t.co/7ptMolzrh6 https://t.co/NRwLwppm5J
 LinkedInVideo
Safeguard Desktop 3.3.0 is out. What is in it, from the release notes: It runs on Electron 45, so it picks up Chromium and Node security updates. Your saved sign-in is now encrypted with your computer's own key (the macOS Keychain, Windows data protection, or the Secret Service…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. What is in it, from the release notes: It runs on Electron 45, so it picks up Chromium and Node security updates. Your saved sign-in is now encrypted with your computer's own key (the macOS Keychain, Windows data protection, or the Secret Service or KWallet on Linux). Nobody is signed out by the change. On Linux, the AppImage runs inside Chromium's sandbox wherever your system allows it, and it no longer needs libfuse2. The Mac builds are signed and notarized. Windows and Linux installers are on the page too, with SHA-256 checksums listed so you can verify what you download. Download it from https://lnkd.in/gvcRpjMi #AppSec #SupplyChainSecurity #DevSecOps
 InstagramVideo
Safeguard Desktop 3.3.0 is out. Electron 45, an encrypted saved sign-in, a sandboxed Linux AppImage. Mac builds are signed and notarized, and SHA-256 checksums are listed for every installer. Download: http://safeguard.sh/download (link in bio) #appsec #devsecops #supplychainsec…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. Electron 45, an encrypted saved sign-in, a sandboxed Linux AppImage. Mac builds are signed and notarized, and SHA-256 checksums are listed for every installer. Download: http://safeguard.sh/download (link in bio) #appsec #devsecops #supplychainsecurity
- YouTubeVideo
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. The Mac builds are signed and notarized. Windows and Linux installers list SHA…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. The Mac builds are signed and notarized. Windows and Linux installers list SHA-256 checksums on the download page. Footage: Mixkit stock (free license), recording of https://na2.hubs.ly/H08LgFP0. Download: https://na2.hubs.ly/H08LgFQ0 #AppSec #DevSecOps #Shorts
- FacebookVideo
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. Mac builds are signed and notarized; Windows and Linux installers list SHA-256…
Read the full postHide the full post
Safeguard Desktop 3.3.0 is out. It runs on Electron 45, encrypts your saved sign-in with your computer's own key, and the Linux AppImage now runs inside Chromium's sandbox where your system allows it. Mac builds are signed and notarized; Windows and Linux installers list SHA-256 checksums so you can verify the download. Download: https://na2.hubs.ly/H08LgJS0
- XVideo
Safeguard Desktop 3.3.0 is out. Electron 45, saved sign-in encrypted with your computer's own key, a sandboxed Linux AppImage. Mac builds signed and notarized, SHA-256 checksums listed. https://t.co/6XVLzIEMJC https://t.co/pTiMCCu7he
- TikTokVideo
Safeguard Desktop 3.3.0 is out: Electron 45, encrypted saved sign-in, sandboxed Linux AppImage, signed and notarized Mac builds. Download at https://na2.hubs.ly/H08LgJY0 (link in bio) #appsec #devsecops
 Instagram
How does a small team fix many repositories at once? Select, run remediation, review one pull request per repository. Only the exceptions need a person. Watch the Short on YouTube, link in bio: http://youtube.com/shorts/ORIvrX0x1LI #AppSec #DevSecOps #SupplyChainSecurity
Read the full postHide the full post
How does a small team fix many repositories at once? Select, run remediation, review one pull request per repository. Only the exceptions need a person. Watch the Short on YouTube, link in bio: http://youtube.com/shorts/ORIvrX0x1LI #AppSec #DevSecOps #SupplyChainSecurity
 Instagram
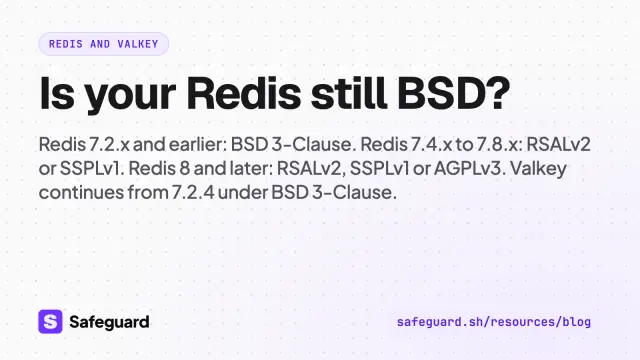
A licence change is a supply chain event. Redis 7.2.x and earlier: BSD 3-Clause. Redis 7.4.x to 7.8.x: RSALv2 or SSPLv1. Redis 8 and later: RSALv2, SSPLv1 or AGPLv3. Valkey continues from Redis 7.2.4 under BSD 3-Clause. Check what your SBOM says about the Redis-compatible server…
Read the full postHide the full post
A licence change is a supply chain event. Redis 7.2.x and earlier: BSD 3-Clause. Redis 7.4.x to 7.8.x: RSALv2 or SSPLv1. Redis 8 and later: RSALv2, SSPLv1 or AGPLv3. Valkey continues from Redis 7.2.4 under BSD 3-Clause. Check what your SBOM says about the Redis-compatible server you run. Not legal advice. Link in bio: http://safeguard.sh/resources/blog/redis-and-valkey-release-history-from-2009-to-redis-8-and-valkey-8-licence-changes-the-fork-and-security-defaults #SBOM #Redis #Valkey #OpenSource
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.