

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Latest posts
RSS feed Instagram
Torq acquired Jit on 19 May 2026. The coverage we read does not say what happens to the standalone Jit product, its contracts or its support. Our guide for AppSec and DevSecOps buyers: what is known, questions to ask in writing, and a 30 day checklist. Link in bio: http://safegu…
Read the full postHide the full post
Torq acquired Jit on 19 May 2026. The coverage we read does not say what happens to the standalone Jit product, its contracts or its support. Our guide for AppSec and DevSecOps buyers: what is known, questions to ask in writing, and a 30 day checklist. Link in bio: http://safeguard.sh/resources/blog #DevSecOps #AppSec #SupplyChainSecurity
- X
Torq acquired Jit on 19 May 2026. Coverage does not say what happens to the standalone product. Sourced buyer guide: what is known, questions to ask in writing, a 30 day checklist. https://t.co/zoDgPQFkvg https://t.co/zYW0REXHPX
 YouTubeVideo
Mellow lo-fi beats for coding, code review and long incident hours. No talk, no ads from us, just focus. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable…
Read the full postHide the full post
Mellow lo-fi beats for coding, code review and long incident hours. No talk, no ads from us, just focus. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardLofi #LofiBeats #FocusMusic #DevSecOps #AppSec #SoftwareSupplyChain
 YouTubeVideo
Short product walkthroughs on a loop, around the clock: generating and managing SBOMs, blocking malicious packages with Package Firewall, scanning your code and containers, and getting fix pull requests that your own CI tests. Watch how Safeguard, the software supply chain secur…
Read the full postHide the full post
Short product walkthroughs on a loop, around the clock: generating and managing SBOMs, blocking malicious packages with Package Firewall, scanning your code and containers, and getting fix pull requests that your own CI tests. Watch how Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams, works in practice. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardDemo #SBOM #PackageFirewall #DevSecOps #AppSec #SoftwareSupplyChain
 YouTubeVideo
Back to back episodes of the Safeguard podcasts, around the clock: Ask Safeguard, The Fix Window, The Audit Window, Patch Monday and Permission Prompt. Practical software supply chain security talk for AppSec, DevSecOps and compliance teams. Safeguard is the software supply chai…
Read the full postHide the full post
Back to back episodes of the Safeguard podcasts, around the clock: Ask Safeguard, The Fix Window, The Audit Window, Patch Monday and Permission Prompt. Practical software supply chain security talk for AppSec, DevSecOps and compliance teams. Safeguard is the software supply chain security platform for those teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardPodcast #AskSafeguard #DevSecOps #AppSec #SoftwareSupplyChain
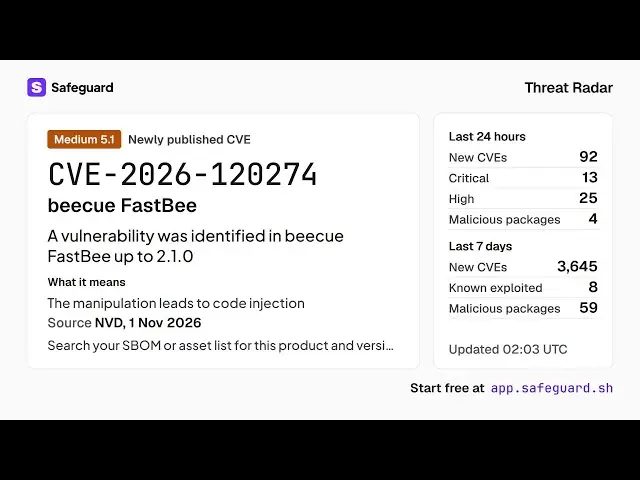 YouTubeVideo
A live, always-on feed of newly published CVEs, CISA Known Exploited Vulnerabilities additions and malicious package reports across npm, PyPI and other registries, drawn as animated cards for AppSec and DevSecOps teams. It reports public advisories and sources, it does not claim…
Read the full postHide the full post
A live, always-on feed of newly published CVEs, CISA Known Exploited Vulnerabilities additions and malicious package reports across npm, PyPI and other registries, drawn as animated cards for AppSec and DevSecOps teams. It reports public advisories and sources, it does not claim Safeguard found any of them. Safeguard is the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream The cards are generated automatically from public advisory and vulnerability data and rendered as animation. No real people are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. Always check the original advisory before acting. #ThreatRadar #CVE #KEV #SupplyChainSecurity #DevSecOps #AppSec
 Instagram
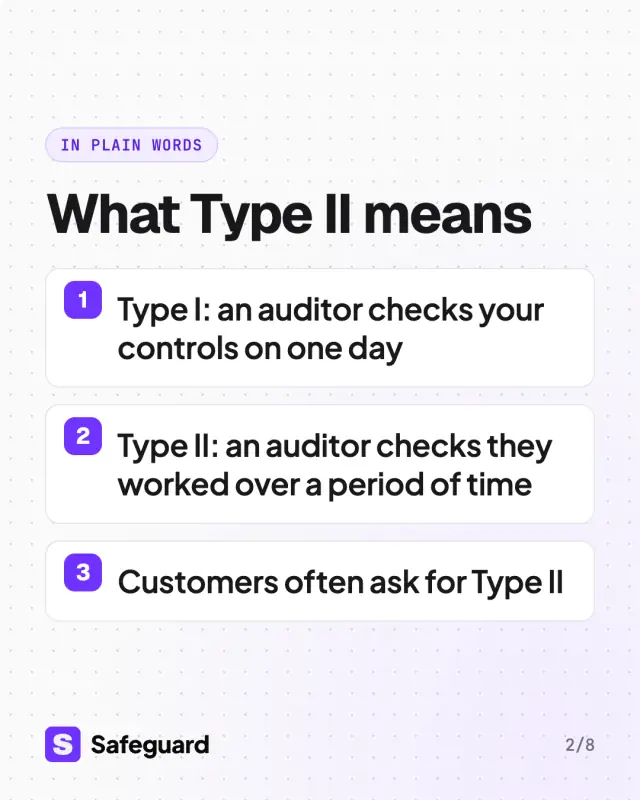
SOC 2 Type II for a startup under 10 people: the checklist. Policies. Access control and reviews. Change management with code review. Vendor review. Vulnerability management. Evidence collection. Security training. Incident response. Automation keeps evidence building as you shi…
Read the full postHide the full post
SOC 2 Type II for a startup under 10 people: the checklist. Policies. Access control and reviews. Change management with code review. Vendor review. Vulnerability management. Evidence collection. Security training. Incident response. Automation keeps evidence building as you ship. Safeguard's plan also covers app and supply chain security. See safeguard.sh/pricing for current plans. Audit fees are separate. Link in bio: http://safeguard.sh/pricing #SOC2 #SOC2TypeII #StartupLife #Founders #SaaS #Compliance #AppSec
 Facebook
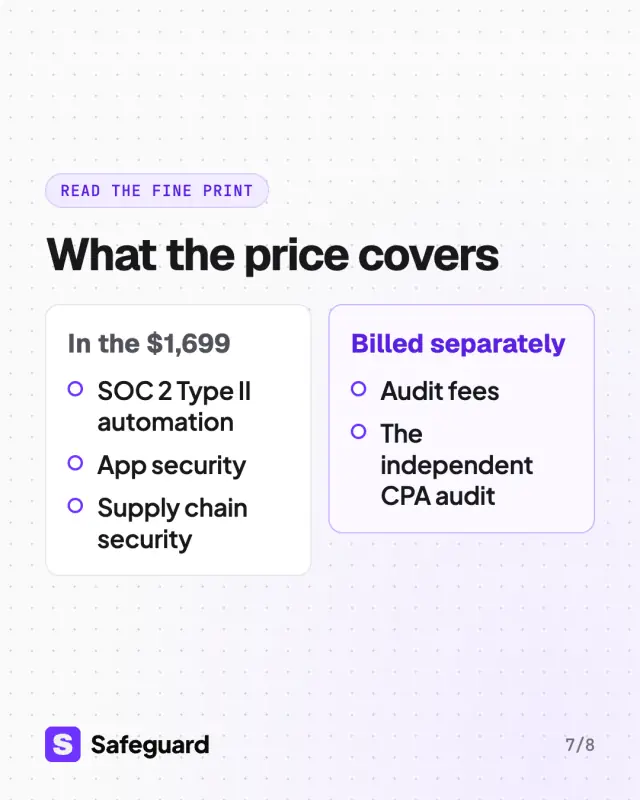
SOC 2 Type II for a startup under 10 people: the checklist. Cover written policies, access control and reviews, change management with code review, vendor review, vulnerability management, evidence collection, security training and incident response. Safeguard's SOC 2 Type II au…
Read the full postHide the full post
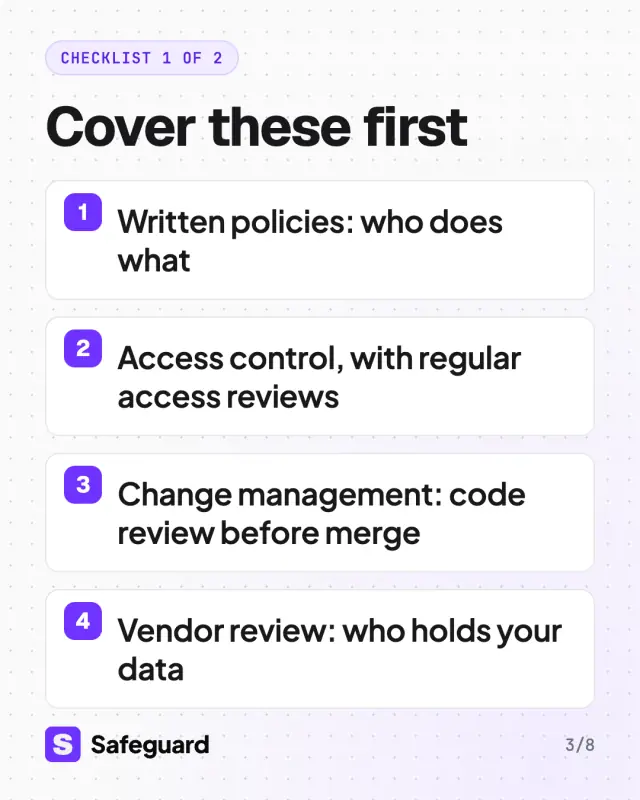
SOC 2 Type II for a startup under 10 people: the checklist. Cover written policies, access control and reviews, change management with code review, vendor review, vulnerability management, evidence collection, security training and incident response. Safeguard's SOC 2 Type II automation also covers app and supply chain security. See https://na2.hubs.ly/H08HZmS0 for current plans. Audit fees are separate. See the plan: https://na2.hubs.ly/H08HZmT0
 LinkedIn
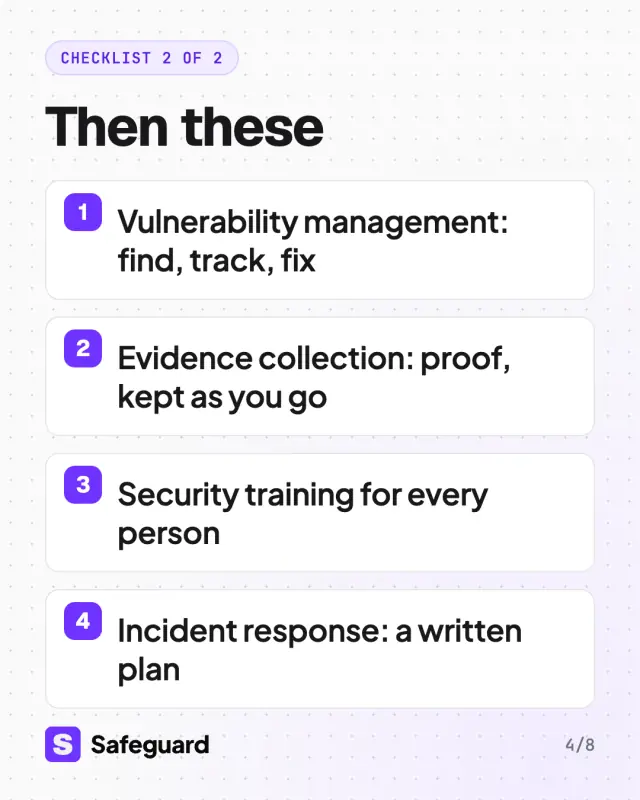
Your first big customer asks for a SOC 2 Type II report. If your team is under 10 people, here is the checklist. SOC 2 Type II means an independent auditor checks that your controls worked over a period of time, not just on one day. For a small team, the work comes down to eight…
Read the full postHide the full post
Your first big customer asks for a SOC 2 Type II report. If your team is under 10 people, here is the checklist. SOC 2 Type II means an independent auditor checks that your controls worked over a period of time, not just on one day. For a small team, the work comes down to eight areas: 1. Written security policies 2. Access control, with regular access reviews 3. Change management, with code review before merge 4. Vendor review 5. Vulnerability management 6. Evidence collection 7. Security training for every person 8. Incident response, as a written plan Automation helps most with evidence. In Safeguard, controls, evidence and tests sit in one place, and tests and evidence collection run on a schedule, so proof builds up while you ship instead of in a scramble before the audit window. The same automation also covers your application and supply chain security. See https://lnkd.in/gZEHux5f for current plans. Plain about the fine print: audit fees are separate, and the plan does not include the independent CPA audit. Swipe through the checklist, then see the plan: https://lnkd.in/gEc4rkAs #SOC2 #StartupSecurity #Compliance #AppSec
 X
SOC 2 Type II checklist for a startup under 10 people: policies, access reviews, code review, vendor review, vulnerability management, evidence, training, incident response. Audit fees are separate. See current plans: https://t.co/6Yw6VeVF7h https://t.co/NjUIJ5Q603
Read the full postHide the full post
SOC 2 Type II checklist for a startup under 10 people: policies, access reviews, code review, vendor review, vulnerability management, evidence, training, incident response. Audit fees are separate. See current plans: https://t.co/6Yw6VeVF7h https://t.co/NjUIJ5Q603
 LinkedIn
Jit runs open source scanners through security plans as code. Safeguard runs its own engines and opens the fix pull request. We are a competitor, so read this as a vendor's view. Jit's strengths, per the page: named scanners you can inspect and test, readable plans, and managed…
Read the full postHide the full post
Jit runs open source scanners through security plans as code. Safeguard runs its own engines and opens the fix pull request. We are a competitor, so read this as a vendor's view. Jit's strengths, per the page: named scanners you can inspect and test, readable plans, and managed execution. Ours: reachability verdicts (reachable, conditionally reachable, unreachable, unknown) and auto-fix that opens policy gated pull requests. Autonomous remediation ships off, and every category starts on Manual. The post also covers when to choose Jit, when to choose Safeguard, and a two week proof of concept checklist. Facts about Jit are as of 28 October 2026 from its docs and announcements. The full comparison: https://lnkd.in/gVVsNRnb
- Instagram
Jit runs open source scanners through security plans as code. Safeguard runs its own engines and opens the fix pull request. We are a competitor, so the post says where Jit is strong and when to choose it. Compared as of 28 October 2026. Link in bio: safeguard.sh/resources/blog
Read the full postHide the full post
Jit runs open source scanners through security plans as code. Safeguard runs its own engines and opens the fix pull request. We are a competitor, so the post says where Jit is strong and when to choose it. Compared as of 28 October 2026. Link in bio: safeguard.sh/resources/blog
- Facebook
Jit orchestrates open source scanners through security plans as code. Safeguard runs its own engines and opens fix pull requests. We are a competitor, so we say where Jit is strong and when to pick it. Compared as of 28 October 2026. The full comparison: https://na2.hubs.ly/H08K…
Read the full postHide the full post
Jit orchestrates open source scanners through security plans as code. Safeguard runs its own engines and opens fix pull requests. We are a competitor, so we say where Jit is strong and when to pick it. Compared as of 28 October 2026. The full comparison: https://na2.hubs.ly/H08K-zF0
- X
Jit: security plans as code over open source scanners. Safeguard: its own engines, and the fix pull request. We are a competitor, so the post says where Jit is strong too. https://t.co/13yiqkvXoh https://t.co/fVbVFeQM7M
- YouTubeVideo
Is it safe to auto-merge dependency fixes, and who approves a pull request that a tool wrote? Mira asks the questions teams raise before they let automatic fixes near their repositories, and Cal answers from Safeguard's published docs and posts: the default is a person reviewing…
Read the full postHide the full post
Is it safe to auto-merge dependency fixes, and who approves a pull request that a tool wrote? Mira asks the questions teams raise before they let automatic fixes near their repositories, and Cal answers from Safeguard's published docs and posts: the default is a person reviewing every fix, auto-merge is opt-in and gated behind passing CI, your tests run before a pull request opens, and transitive dependencies are fixed by the smallest change that works, with fork and patch when upstream has no fix. For AppSec leads, DevSecOps teams, platform engineers and engineering managers evaluating autonomous remediation, auto-fix pull requests and AI vulnerability remediation. Topics: automatic fix pull requests, autonomous remediation, auto-merge, dependency updates, transitive dependencies, npm overrides, fork and patch, bulk remediation, CI, human review, reachability, software supply chain security, security podcast, cybersecurity podcast, AppSec podcast, DevSecOps podcast. Chapters: 00:00 Cold open 00:26 Intro 00:48 Question 1: Is it safe to auto-merge dependency fixes? 01:42 Question 2: Who approves and merges a fix pull request? 02:33 Question 3: Does it run my tests before it opens a pull request? 03:22 Question 4: How do I fix a transitive dependency without waiting for the maintainer? 04:16 Question 5: How do I control which fixes apply automatically? 05:09 Question 6: Can I fix many repositories at once? 05:53 Recap and call to action 06:09 Outro Links: Safeguard: https://safeguard.sh/?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05 More episodes: https://safeguard.sh/podcast?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05 Listen on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc?utm_source=podcast&utm_medium=video&utm_campaign=ask-safeguard&utm_content=ep05
 YouTubeVideo
No talk, no ads from us, just focus. Built by Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate a…
Read the full postHide the full post
No talk, no ads from us, just focus. Built by Safeguard, the software supply chain security platform for AppSec, DevSecOps and compliance teams. Start free: https://app.safeguard.sh What Safeguard does Find vulnerable and risky open source in your code and containers, generate and manage SBOMs, block malicious, typosquatted and dependency confusion packages before they reach your build with Package Firewall, and get fix pull requests that your own CI tests. Gold gives you hardened open source components with signed builds and SLSA provenance. Compliance automation helps you prepare for SOC 2 and similar frameworks with continuous evidence. Platform: https://safeguard.sh/platform Pricing: https://safeguard.sh/pricing Docs: https://docs.safeguard.sh Desktop and CLI downloads: https://safeguard.sh/download Trust and security Safeguard is SOC 2 Type I and Type II audited. Trust Center: https://trust.safeguard.sh Learn more Blog: https://safeguard.sh/resources/blog Ask Safeguard podcast on YouTube: https://www.youtube.com/playlist?list=PLU75J30d_nPE The Fix Window on Spotify: https://open.spotify.com/show/03400iIvo19RZbfRDfPECc The Audit Window on Spotify: https://open.spotify.com/show/03400grx1OHf5tmZ1qrsdb Patch Monday on Spotify: https://open.spotify.com/show/1m9VhuuSqCzDKxH03E97fn Permission Prompt on Spotify: https://open.spotify.com/show/4BN9zeR2XXtDGANjpIMVEx Ask Safeguard on Spotify: https://open.spotify.com/show/447mcxAAIcsX29zUzutRoL Work with us Partners (resellers, MSSPs, consultancies): https://safeguard.sh/company/partners Talk to the team: https://safeguard.sh/contact About this stream No real people, places or events are shown. It runs around the clock; if it ever drops, it comes back on its own within a minute or two. #SafeguardFM #AmbientMusic #FocusMusic #DevSecOps #AppSec #SoftwareSupplyChain
 InstagramVideo
US clocks go back this Sunday at 2:00 local time. One host holds many copies of time zone data: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review local time jobs, and list the tzdata version in every image. Link in bio: http://safeguard.sh/resources/blo…
Read the full postHide the full post
US clocks go back this Sunday at 2:00 local time. One host holds many copies of time zone data: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review local time jobs, and list the tzdata version in every image. Link in bio: http://safeguard.sh/resources/blog #sre #devops #platformengineering #daylightsaving
 LinkedInVideo
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your code through the IANA time zone database, and only when an update carries it. Release 2026e is the current one. It includes the last of four Canadian changes to permanent standard time, so older…
Read the full postHide the full post
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your code through the IANA time zone database, and only when an update carries it. Release 2026e is the current one. It includes the last of four Canadian changes to permanent standard time, so older data can still move a clock back where it should not. The catch is that one host usually holds several independent copies of that data: the OS zoneinfo files, a Java runtime's own copy, Node and browser ICU, a Python tzdata package, Go's embedded data. They can disagree. A short check before the weekend: Run zdump on a few zones, per host and per runtime. Keep storage and logs in UTC. Review jobs scheduled in local time, because 1:30 happens twice. List the tzdata version in every image. A stale rule is not a CVE, so a vulnerability scanner will not flag it. An SBOM will list it, which is where Safeguard fits: scan images, repositories and SBOMs and see which ones still carry an older copy. Full walkthrough with commands: https://lnkd.in/gJXQtdZ8 #SRE #PlatformEngineering #DevOps
 YouTubeVideo
US clocks go back this Sunday, 1 November, at 2:00 local time. The IANA time zone database carries that rule to your servers, phones and code, but only when an update ships it. One host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in U…
Read the full postHide the full post
US clocks go back this Sunday, 1 November, at 2:00 local time. The IANA time zone database carries that rule to your servers, phones and code, but only when an update ships it. One host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review jobs scheduled in local time, and list the tzdata version in every image. Footage: NIST (public domain, via Wikimedia Commons), Mixkit stock (free license), local terminal recording, IANA release notes. Walkthrough: https://na2.hubs.ly/H08Ks350 #SRE #DevOps #Shorts
- FacebookVideo
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your servers, phones and code through the IANA time zone database, and one host often holds several copies of that data (OS, Java, Node, Python, Go). Before the weekend: run zdump on a few zones, kee…
Read the full postHide the full post
US clocks go back this Sunday, 1 November, at 2:00 local time. The rule reaches your servers, phones and code through the IANA time zone database, and one host often holds several copies of that data (OS, Java, Node, Python, Go). Before the weekend: run zdump on a few zones, keep logs in UTC, review jobs scheduled in local time, and list the tzdata version in every image. An SBOM can show you which images carry an older copy. Walkthrough with commands: https://na2.hubs.ly/H08JFD10
- XVideo
US clocks go back Sunday 1 November at 2:00 local time. The rules reach your hosts through tzdata, and one host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review local time jobs. https://t.co/Af3Cp8LHxg https://t.co/ZECoyDc5g3
- TikTokVideo
US clocks go back Sunday. One host holds many copies of tz data: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review local time jobs. Link in bio: https://na2.hubs.ly/H08JFHL0 #sre #devops #daylightsaving
 Instagram
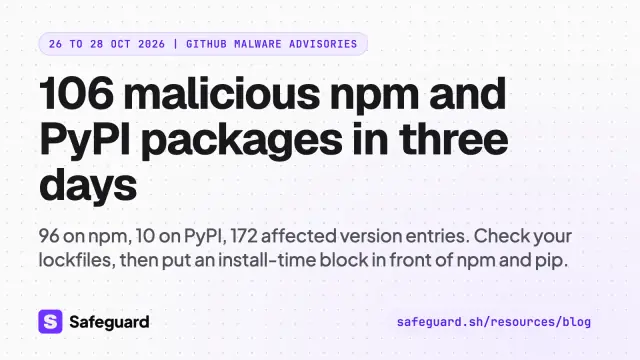
106 malicious npm and PyPI packages in three days, 26 to 28 October 2026, per GitHub's advisory database. 96 on npm, 10 on PyPI. Check your lockfiles, clean up if you hit one, and put an install-time block in front of npm and pip. Safeguard's Package Firewall may block malicious…
Read the full postHide the full post
106 malicious npm and PyPI packages in three days, 26 to 28 October 2026, per GitHub's advisory database. 96 on npm, 10 on PyPI. Check your lockfiles, clean up if you hit one, and put an install-time block in front of npm and pip. Safeguard's Package Firewall may block malicious, typosquatted and dependency-confusion packages before any install script runs. Link in bio: http://safeguard.sh/resources/blog #npm #PyPI #SupplyChainSecurity
- LinkedIn
106 malicious npm and PyPI packages in three days. GitHub's advisory database published them between 26 and 28 October. 96 are on npm and 10 on PyPI, across 172 affected version entries. Several were pulled within minutes. Others were built to hurt: an install-time Monero miner…
Read the full postHide the full post
106 malicious npm and PyPI packages in three days. GitHub's advisory database published them between 26 and 28 October. 96 are on npm and 10 on PyPI, across 172 affected version entries. Several were pulled within minutes. Others were built to hurt: an install-time Monero miner that persists through systemd, a dependency-confusion beacon aimed at internal package scopes, and PyPI infostealers. Check your lockfiles first. The post has a script that does it, plus cleanup steps if you find a hit. Then put a control on the fetch path. Safeguard's Package Firewall sits in front of npm and pip and may block malicious, typosquatted and dependency-confusion packages before any install script runs. To be clear, the packages in this batch were found by others, not by Safeguard. What they did and how to block the next batch: https://lnkd.in/gWwJkFs9 #npm #PyPI #SupplyChainSecurity
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.