

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on X
RSS feed XVideo
Every dev team knows the feeling. The security scan comes back with thousands of issues and nobody knows where to start. Here's the thing: most of those issues sit in code your app never touches. Safeguard scans your code and dependencies, works out what's actually reachable, an…
Read the full postHide the full post
Every dev team knows the feeling. The security scan comes back with thousands of issues and nobody knows where to start. Here's the thing: most of those issues sit in code your app never touches. Safeguard scans your code and dependencies, works out what's actually reachable, and https://t.co/XeUO6Vk6c4
 XVideo
Your CVE dashboard is all green. That’s the part that should worry you. Closing every known CVE proves you handled the vulnerabilities that already have a name. A zero-day is the one that doesn’t, so it never shows up on the board you hand the auditor. When a customer’s security…
Read the full postHide the full post
Your CVE dashboard is all green. That’s the part that should worry you. Closing every known CVE proves you handled the vulnerabilities that already have a name. A zero-day is the one that doesn’t, so it never shows up on the board you hand the auditor. When a customer’s security https://t.co/UHS6yDk7hk
 XVideo
Your team ships more code every week. Your scanner only knows last year’s CVEs. A scanner matches known vulnerabilities. But the one that actually hurts, the flaw an AI just wrote into your codebase, doesn’t have a CVE yet. No advisory, no signature, nothing to match. So we buil…
Read the full postHide the full post
Your team ships more code every week. Your scanner only knows last year’s CVEs. A scanner matches known vulnerabilities. But the one that actually hurts, the flaw an AI just wrote into your codebase, doesn’t have a CVE yet. No advisory, no signature, nothing to match. So we built https://t.co/YCMm3CZ8PX
 XVideo
That notification badge you’ve been ignoring for three weeks is doing more work than you think. The scariest bugs in your software aren’t the ones with a CVE and a patch waiting. They’re the ones nobody’s named yet, quietly worth more on the open market than most engineers make…
Read the full postHide the full post
That notification badge you’ve been ignoring for three weeks is doing more work than you think. The scariest bugs in your software aren’t the ones with a CVE and a patch waiting. They’re the ones nobody’s named yet, quietly worth more on the open market than most engineers make https://t.co/SsBhh7ORj6
 XVideo
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s https:…
Read the full postHide the full post
The vulnerability that gets you won’t have a CVE yet. No CVE means no patch, no advisory, and nothing for a scanner to match against. That’s a zero-day, and it’s already sitting in your dependencies. So we built Safeguard to find the flaw before the CVE exists, prove it’s https://t.co/AW4IbRZ0Ss
 X
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like. https://t.co/uLcJ0yeoTu
Read the full postHide the full post
CAPTION: Found something before it even has a CVE number? It still gets a name, an advisory, and a suggested fix attached to it. Comment "ADVISORY" and we'll show you what one looks like. https://t.co/uLcJ0yeoTu
- X
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify
Read the full postHide the full post
Finding it is only step one. After that, it gets checked, tagged, and disclosed the responsible way before it ever hits a public feed. Because discovering a vulnerability means nothing if the process after discovery puts more people at risk. Safeguard can help your team identify
 XVideo
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs https:/…
Read the full postHide the full post
A long list of findings can look impressive, but what really matters is knowing which ones are actually worth fixing. Safeguard challenges findings and proposed fixes before they move forward, helping cut through the noise and give your team more confidence in what needs https://t.co/EHV535RlVA
 XVideo
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard https:/…
Read the full postHide the full post
Some vulnerabilities don’t look dangerous at first. They can sit quietly in perfectly normal-looking code until the right conditions turn them into something exploitable. That’s why finding the unusual paths matters, not just checking for what we already know. #safeguard https://t.co/PASPxRxwIN
- X
The bugs that scare me aren't the ones with a CVE number. They're the ones nobody has named yet. Sitting in a dependency someone shipped two years ago and stopped thinking about. There's no patch to apply, because there's nothing to patch against. Your scanner reads NVD, GHSA and
Read the full postHide the full post
The bugs that scare me aren't the ones with a CVE number. They're the ones nobody has named yet. Sitting in a dependency someone shipped two years ago and stopped thinking about. There's no patch to apply, because there's nothing to patch against. Your scanner reads NVD, GHSA and
 XVideo
Vulnerability feeds tell you what’s already known. Zero-day discovery starts with what isn’t. Safeguard Research looks beyond published threats—investigating package behavior, maintainers, tampering, and provenance. Because real security starts before the alert. https://t.co/Yet…
Read the full postHide the full post
Vulnerability feeds tell you what’s already known. Zero-day discovery starts with what isn’t. Safeguard Research looks beyond published threats—investigating package behavior, maintainers, tampering, and provenance. Because real security starts before the alert. https://t.co/YetKu84Ovg
 XVideo
A Zero Day nobody’s found yet is a gift — to whoever finds it first. Left hidden, it’s an open door. Found and fixed first, it’s the reason your software holds. Zero Days aren’t only threats. Found first, they’re your best defense. Safeguard & self-heal your software supply…
Read the full postHide the full post
A Zero Day nobody’s found yet is a gift — to whoever finds it first. Left hidden, it’s an open door. Found and fixed first, it’s the reason your software holds. Zero Days aren’t only threats. Found first, they’re your best defense. Safeguard & self-heal your software supply chain https://t.co/Ljfq1IM1eR
 XVideo
By the time a vulnerability has a name, the attackers already have it Safeguard finds it before it’s public and fixes it for you — before the CVE even exists. Book a demo → https://t.co/hGBVx0ueaC #cybersecurity #zeroday #devsecops #coding #techtok https://t.co/Jy3n4MG3I5
Read the full postHide the full post
By the time a vulnerability has a name, the attackers already have it Safeguard finds it before it’s public and fixes it for you — before the CVE even exists. Book a demo → https://t.co/hGBVx0ueaC #cybersecurity #zeroday #devsecops #coding #techtok https://t.co/Jy3n4MG3I5
 XVideo
Not every team can run AI on their code, and we get that. So Zero-Day Discovery works two ways. One powered by AI, one that isn't. Same protection, either way. Comment "MODES" and we'll walk you through both. https://t.co/65HuxNWfkU
Read the full postHide the full post
Not every team can run AI on their code, and we get that. So Zero-Day Discovery works two ways. One powered by AI, one that isn't. Same protection, either way. Comment "MODES" and we'll walk you through both. https://t.co/65HuxNWfkU
 X
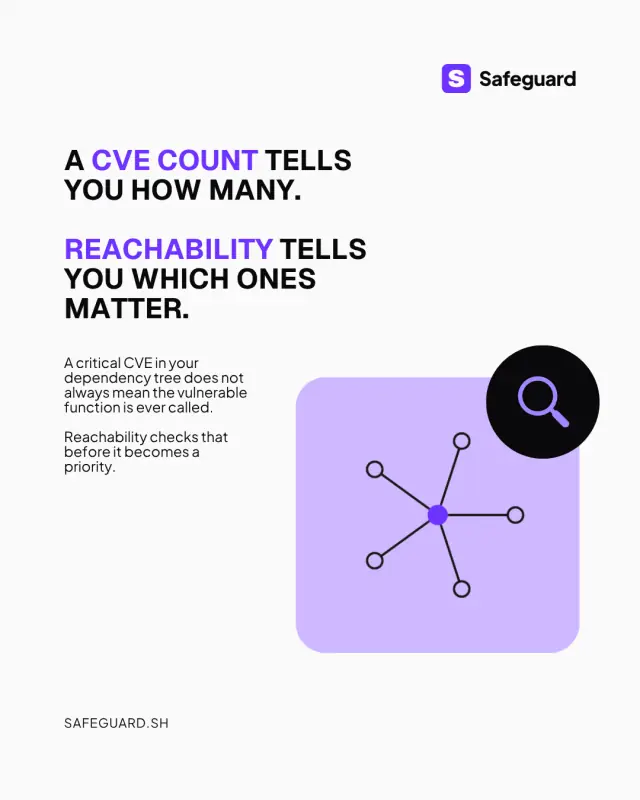
A critical CVE might exist in your dependency tree, but that does not always mean it is actually reachable in your application. Reachability helps you understand what truly matters, so your team can focus on fixing the risks that can actually affect your software. Are you https:…
Read the full postHide the full post
A critical CVE might exist in your dependency tree, but that does not always mean it is actually reachable in your application. Reachability helps you understand what truly matters, so your team can focus on fixing the risks that can actually affect your software. Are you https://t.co/SaT12oUlmE
 XVideo
Ask your scanner one question: where does my code go when you run it? If the answer bugs you, that’s why Safeguard CLI exists. Book a demo on your own repo: https://t.co/irXaFjRMEi #AppSec #DevSecOps https://t.co/GyJWRRRY33
Read the full postHide the full post
Ask your scanner one question: where does my code go when you run it? If the answer bugs you, that’s why Safeguard CLI exists. Book a demo on your own repo: https://t.co/irXaFjRMEi #AppSec #DevSecOps https://t.co/GyJWRRRY33
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.