

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on X
RSS feed X
Three US software security dates ahead: CMMC Phase 2 on 10 Nov 2026, CISA BOD 26-04 timelines on 7 Dec, Colorado AI developer duties on 1 Jan 2027. Each rule from its primary text, plus a 90-day plan: https://t.co/ctRZjlSt4e https://t.co/1F4UxoNS7Y
 XVideo
One vendor breach, two universities. NEC says a company it outsources to was attacked and valid accounts were misused against its customers. Your risk includes your vendors' vendors. Can you name them all? https://t.co/ChMynlS07w https://t.co/WIzPYf6JAn
 X
Anthropic's S-1 (filed 26 Oct) reads like a vendor security review answered in public: weights named a state-sponsored target, "known limitations or gaps" in defenses, agent hijack paths, dated outages. What it means for teams on Claude: https://t.co/kYmYhSmUL9
 X
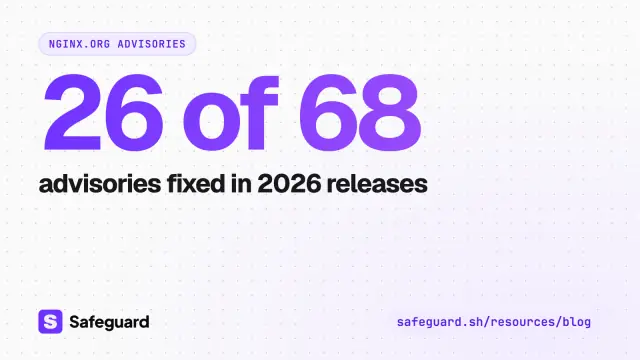
26 of the 68 advisories on the nginx advisories page were fixed in 2026 releases. Patch cadence is the easy part. Which nginx build runs in each image and host? Distro and container packagers set your timing. An SBOM turns that into a lookup. https://t.co/HPKunwnOsJ https://t.co…
Read the full postHide the full post
26 of the 68 advisories on the nginx advisories page were fixed in 2026 releases. Patch cadence is the easy part. Which nginx build runs in each image and host? Distro and container packagers set your timing. An SBOM turns that into a lookup. https://t.co/HPKunwnOsJ https://t.co/NknU87J0E5
- X
Taking a security platform enterprise-wide? SSO, SCIM, scoped roles, org hierarchy, staged gates and a SIEM-streamable audit log, with a phased plan for the platform owner. https://t.co/3x3lkfvy7V
 XVideo
stolen GitHub tokens push one sync-check workflow, print every reachable secret encoded and delete the run. 13,500+ branches, 850+ accounts. GitHub's approval hold covers public repos, not private repos or GHES. what to check today: https://t.co/aigmreqJPQ https://t.co/5Y9qgKFsnU
- X
Where does your code go when you adopt a security platform? Deployment by deployment: SaaS (US, EU Frankfurt, Gov), private VPC, on-prem, air-gapped, and what leaves your network in each. https://t.co/IOfxXXRVA6
 XVideo
28 October: Node.js 26 moves to LTS and Node.js 27 starts its Alpha phase. A good day to check which Node line every service runs. 22 ends 30 Apr 2027, 20 already ended. https://t.co/bHfBYkxqce https://t.co/kWFgJpmTRF
 X
Connecting a code host covers the code. It does not cover the images already in your registry, the models in a cloud AI account or the SBOM a supplier sent you. A map of every Safeguard integration, with a rollout order: https://t.co/NKDnXC0qYS https://t.co/2oYz7Zg7GM
 XVideo
An MCP Registry listing proves who published the record. Not who runs the endpoint, and not that the server is safe. We're now listed as sh.safeguard/safeguard, so check us like anyone: name over title, reverse the namespace, match the URL to our docs. https://t.co/P0SuczuNFg ht…
Read the full postHide the full post
An MCP Registry listing proves who published the record. Not who runs the endpoint, and not that the server is safe. We're now listed as sh.safeguard/safeguard, so check us like anyone: name over title, reverse the namespace, match the URL to our docs. https://t.co/P0SuczuNFg https://t.co/EAvzeW5bni
 X
CVE-2026-114625, SQL injection in on-prem Arista VeloCloud Orchestrator, is in CISA KEV (23 Oct). Today: 1) on-prem, not Hosted? 2) build at 5.2.3.18, 6.1.3.10 or 6.4.2.12 or later? 3) portal limited to admin networks, logs reviewed? https://t.co/thMtrqRtBN https://t.co/Iz791ryy…
Read the full postHide the full post
CVE-2026-114625, SQL injection in on-prem Arista VeloCloud Orchestrator, is in CISA KEV (23 Oct). Today: 1) on-prem, not Hosted? 2) build at 5.2.3.18, 6.1.3.10 or 6.4.2.12 or later? 3) portal limited to admin networks, logs reviewed? https://t.co/thMtrqRtBN https://t.co/Iz791ryy2K
 XVideo
People hold about four chunks in working memory. Some models hold a million tokens, word for word. The risk isn't memory. Instructions and data share one channel, so a web page or a tool result sitting in context can steer an agent. https://t.co/rIpuBNjrur
Read the full postHide the full post
People hold about four chunks in working memory. Some models hold a million tokens, word for word. The risk isn't memory. Instructions and data share one channel, so a web page or a tool result sitting in context can steer an agent. https://t.co/rIpuBNjrur
- XVideo
SOC 2 Type II automation for startups under 10 people: $1,699 a year, flat. Established tools start around $4,000 to $15,000. Same plan covers your app and supply chain security. Audit fees are separate. https://t.co/MuSxHZZb9p https://t.co/93coQlJxxz
Read the full postHide the full post
SOC 2 Type II automation for startups under 10 people: $1,699 a year, flat. Established tools start around $4,000 to $15,000. Same plan covers your app and supply chain security. Audit fees are separate. https://t.co/MuSxHZZb9p https://t.co/93coQlJxxz
 X
Safeguard's partner program is open worldwide. 30% margin in year one, 35% on registered deals. Resell, white-label, co-sell or offer managed services. https://t.co/m3PcKklSiG https://t.co/Sz6ArUjAfS
 XVideo
A Zero Day has no CVE, so a scanner that only matches public feeds has nothing to match. Run a loop instead of a ticket queue: detect, decide, fix, source a safe component, verify, prevent. People set the rules. https://t.co/PMf9ymrLTq https://t.co/46FxomXyNS
Read the full postHide the full post
A Zero Day has no CVE, so a scanner that only matches public feeds has nothing to match. Run a loop instead of a ticket queue: detect, decide, fix, source a safe component, verify, prevent. People set the rules. https://t.co/PMf9ymrLTq https://t.co/46FxomXyNS
 X
OpenCode Console Breach: Rotate Your OpenAI, Anthropic and Google Keys https://t.co/y9tLolXcjN
Read the full postHide the full post
OpenCode Console Breach: Rotate Your OpenAI, Anthropic and Google Keys https://t.co/y9tLolXcjN
 X
Most data doesn't leak in some dramatic hack scene. It leaks quietly, through a vulnerability nobody was watching for yet. Zero-day discovery runs its own research pipeline to catch these before they're public knowledge, so the window where you're exposed gets a lot smaller. htt…
Read the full postHide the full post
Most data doesn't leak in some dramatic hack scene. It leaks quietly, through a vulnerability nobody was watching for yet. Zero-day discovery runs its own research pipeline to catch these before they're public knowledge, so the window where you're exposed gets a lot smaller. https://t.co/o2hjBVQprQ
 X
Customers don't see your infrastructure. They just see whether their information stayed theirs. Catching a vulnerability before it's exploited isn't just a technical task, it's what keeps that trust intact. See how early detection protects it. https://t.co/sKwsjYPi4U
Read the full postHide the full post
Customers don't see your infrastructure. They just see whether their information stayed theirs. Catching a vulnerability before it's exploited isn't just a technical task, it's what keeps that trust intact. See how early detection protects it. https://t.co/sKwsjYPi4U
- X
CI/CD is the most dangerous trust boundary in most orgs and barely shows up in security reviews. it runs as a privileged process, fetches dependencies at build time with no runtime check, and has write access to production. a malicious package there isn't a dev machine problem.
- X
dependency confusion works because private package names are predictable. typosquatting works because attention is finite. neither requires a sophisticated attacker. a weekend and a registry account is enough. the bar to compromise a build pipeline is lower than most teams think.
- X
the SBOM gives you a receipt. it doesn't tell you if what you bought is safe. knowing you have lodash 4.17.21 is useful. knowing whether that specific build of lodash was tampered with in the registry before you pulled it is a different question entirely, and most SBOMs don't
Read the full postHide the full post
the SBOM gives you a receipt. it doesn't tell you if what you bought is safe. knowing you have lodash 4.17.21 is useful. knowing whether that specific build of lodash was tampered with in the registry before you pulled it is a different question entirely, and most SBOMs don't
- X
vibe coding didn't create the supply chain problem. it just removed the last human who was skimming the dependency list before hitting install. that human wasn't doing a great job. but they were doing something. now there's nobody.
Read the full postHide the full post
vibe coding didn't create the supply chain problem. it just removed the last human who was skimming the dependency list before hitting install. that human wasn't doing a great job. but they were doing something. now there's nobody.
- X
most orgs are solving the wrong supply chain problem. they scan for known CVEs. they block packages on the NIST list. they feel covered. but the actual attacks in 2026 don't use known CVEs. they use packages with no CVE, no history, and clean provenance. a fresh malicious
Read the full postHide the full post
most orgs are solving the wrong supply chain problem. they scan for known CVEs. they block packages on the NIST list. they feel covered. but the actual attacks in 2026 don't use known CVEs. they use packages with no CVE, no history, and clean provenance. a fresh malicious
- X
Safeguard Superintelligence Lab https://t.co/VzDuqd35g9
Read the full postHide the full post
Safeguard Superintelligence Lab https://t.co/VzDuqd35g9
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.