

Safeguard on social
Every post we have published on our social profiles, newest first, with the copy exactly as posted. Each card links to the original post.
Posts on X
RSS feed X
Safeguard Lo-fi is live: beats to code to, 24/7. For long sessions, commits and review queues. Press play. https://t.co/VYhg4xjwyY https://t.co/vlcuRp3jWW
 X
Write the exit decision before day one. Our 30 day proof of value plan: scope small, SBOMs and findings in week two, gates in warn mode in week three, a written yes, extend or no in week four. https://t.co/QoEUyOsP5d https://t.co/biln2PEnzZ
 XVideo
What changed in this release? Generate an SBOM per release in CI with safeguard ci scan, publish a copy in Portal, then diff two releases: added components, version changes, new vulnerabilities. Pipeline and caveats: https://t.co/XXp1LoIeJc https://t.co/ImDDGPUctP
 X
Safeguard founder Hritik Kumar Sharma visited TechD in Ahmedabad, June 17 to 19, 2026, and met founder and CEO Sunny Vaghela. Safeguard's platform powers TechD's Provenance AI. Press release: https://t.co/K5QZrrSPIw https://t.co/45xA0tQqaO
 X
Torq acquired Jit on 19 May 2026. Coverage does not say what happens to the standalone product. Sourced buyer guide: what is known, questions to ask in writing, a 30 day checklist. https://t.co/zoDgPQFkvg https://t.co/zYW0REXHPX
 X
SOC 2 Type II checklist for a startup under 10 people: policies, access reviews, code review, vendor review, vulnerability management, evidence, training, incident response. Audit fees are separate. See current plans: https://t.co/6Yw6VeVF7h https://t.co/NjUIJ5Q603
Read the full postHide the full post
SOC 2 Type II checklist for a startup under 10 people: policies, access reviews, code review, vendor review, vulnerability management, evidence, training, incident response. Audit fees are separate. See current plans: https://t.co/6Yw6VeVF7h https://t.co/NjUIJ5Q603
 X
Jit: security plans as code over open source scanners. Safeguard: its own engines, and the fix pull request. We are a competitor, so the post says where Jit is strong too. https://t.co/13yiqkvXoh https://t.co/fVbVFeQM7M
 XVideo
US clocks go back Sunday 1 November at 2:00 local time. The rules reach your hosts through tzdata, and one host often holds several copies: OS, Java, Node, Python, Go. Check each with zdump, keep logs in UTC, review local time jobs. https://t.co/Af3Cp8LHxg https://t.co/ZECoyDc5g3
 X
106 malicious npm and PyPI packages in 3 days (26 to 28 Oct, per GitHub advisories). Miner, dependency-confusion beacon, infostealers. Lockfile check script and install-time blocks: https://t.co/drQPDN2UkI https://t.co/7DeWh5NzZo
 X
CISA added CVE-2026-110447 to KEV on 23 Oct: unauthenticated command injection in richdocumentscode, the Nextcloud built-in Collabora CODE app. Fixed in 26.4.303. It is a PHP app inside Nextcloud. Is it in your SBOM? https://t.co/QS1cjrvhhV https://t.co/JxPhs0SVQP
 XVideo
Before you add a dependency, look it up. https://t.co/wtdVVD7lqE shows the indexed version, known vulns and the Scorecard grade, free, no login. Then check that version against your PR and read the license and install scripts. https://t.co/bCEGAylU2w https://t.co/gEunHUSBmd
 X
Your board does not need 4,000 findings. Two numbers: KEV open in production (should read zero) and time to remediate. One Program Overview page weekly, one scheduled board pack monthly, PDF plus JSON. https://t.co/BPZtPL6dgT https://t.co/5hdozlyDH5
 XVideo
Your coding agents already emit telemetry. Send OpenAI Codex or Claude Code OpenTelemetry to Safeguard and see sessions, tool decisions, model calls and cost, plus AI detections your SOC can act on. Send-only token, credentials redacted. https://t.co/FkOFlO6ur6 https://t.co/O7U2…
Read the full postHide the full post
Your coding agents already emit telemetry. Send OpenAI Codex or Claude Code OpenTelemetry to Safeguard and see sessions, tool decisions, model calls and cost, plus AI detections your SOC can act on. Send-only token, credentials redacted. https://t.co/FkOFlO6ur6 https://t.co/O7U2fSmu93
 X
Revoking a compromised CA is not the fix. The key can sign its own CRLs and OCSP "good" answers. Replace certs and remove trust. Apps with bundled CA lists or pinned keys ignore OS trust store changes. Runbook: https://t.co/8SZQss8SIg https://t.co/xU4VakRsiN
 XVideo
Atlassian's October bulletin: 75 unique CVEs, all in bundled libraries like Tomcat, Netty and Bouncy Castle. The software you buy ships open source too, so you inherit its dependencies. Know what is inside each vendor product and which version you run. https://t.co/WNLaHEwXlC ht…
Read the full postHide the full post
Atlassian's October bulletin: 75 unique CVEs, all in bundled libraries like Tomcat, Netty and Bouncy Castle. The software you buy ships open source too, so you inherit its dependencies. Know what is inside each vendor product and which version you run. https://t.co/WNLaHEwXlC https://t.co/wwsdZLhPnP
 X
CVE-2026-113788: any Lagoon user can run code via the core ssh service. Every release before 2.33.2 is affected; 2.33.1 has no fix. Patch to 2.33.2 or disable the ssh service. No exploitation reported in the sources we checked. https://t.co/pK9DxjmWCX https://t.co/3yZ0hbXCxv
 X
Upstream has not shipped a fix? Two gaps: a fix that has not reached your builds, and no fix at all. SBOM per build, tested remediation PRs, and for no-fix cases a hardened Gold fork. Limit: vendor appliances still need the vendor. https://t.co/u5A9jr4DZb https://t.co/8St5JJUiTe
- XVideo
Your forgotten router is an attack surface. ASUS fixed three High rated flaws on 23 Oct: CVE-2026-93489 auth bypass, CVE-2026-75775 and CVE-2026-75779 root commands. CVE records list a firmware series, no fixed version. How many routers do you own? https://t.co/QKWAiTYTdv https:…
Read the full postHide the full post
Your forgotten router is an attack surface. ASUS fixed three High rated flaws on 23 Oct: CVE-2026-93489 auth bypass, CVE-2026-75775 and CVE-2026-75779 root commands. CVE records list a firmware series, no fixed version. How many routers do you own? https://t.co/QKWAiTYTdv https://t.co/LPqtfIqwxC
 X
Amadeus, Oct 2026: Korean Air and Asiana cite misuse of an Amadeus system account login; heise found an unauthenticated Spring Boot heap dump. No source links them. Ask your vendors which system accounts reach your data and how credentials rotate. https://t.co/SNKF0W3NP8 https:/…
Read the full postHide the full post
Amadeus, Oct 2026: Korean Air and Asiana cite misuse of an Amadeus system account login; heise found an unauthenticated Spring Boot heap dump. No source links them. Ask your vendors which system accounts reach your data and how credentials rotate. https://t.co/SNKF0W3NP8 https://t.co/PTQljXSY9A
 XVideo
The Fix Window, Ep 5 is live: how fast to patch a bug that is already being used. Four facts from CISA's BOD 26-04, and six things to do this week. AI voices. https://t.co/l6T3vu3hVs https://t.co/fl2vzPurB3
 XVideo
One mistyped package name, stopped before it lands. Safeguard's Package Firewall sits between devs, CI and the public registries for npm and pip and blocks malicious, typosquatted and dependency confusion packages at install time. https://t.co/aTgnUYr1eN https://t.co/PhTySVLHFR
 XVideo
Whether your team standardised on Anthropic's Claude or OpenAI's ChatGPT, the risk is one provider (1/3). In Safeguard you pick the model per task: one OpenAI-compatible endpoint, change the id, not the integration. https://t.co/V4OX8DPS18 https://t.co/S7HrD6wMYc
 X
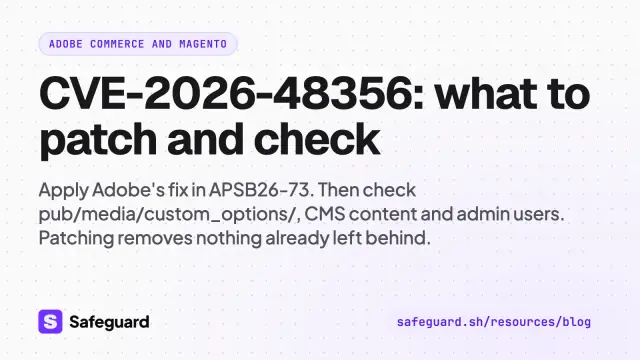
Adobe Commerce/Magento CVE-2026-48356 (CVSS 9.3, file upload): apply Adobe's fix in APSB26-73, then check pub/media/custom_options/ for uploaded files and review admin users. Patching removes nothing already left behind. https://t.co/6WEAkn2pa0 https://t.co/I58Kd7CZpG
 XVideo
OpenSSL 3.4 lost upstream support on 22 Oct. 3.6 loses it Sunday, 1 Nov. The risk is OpenSSL you build, bundle or brew yourself, and base images nobody rebuilt. List every copy and version, then move to 3.5 LTS, 4.0 or 4.1. https://t.co/WtvLfTjxmS https://t.co/RfUvnpNeCV
Follow Safeguard

Self-healing security runs on Safeguard.
Your first fix PR is minutes away.
No sales call required, even your agent can complete the purchase over MCP.